 Safa Marwah
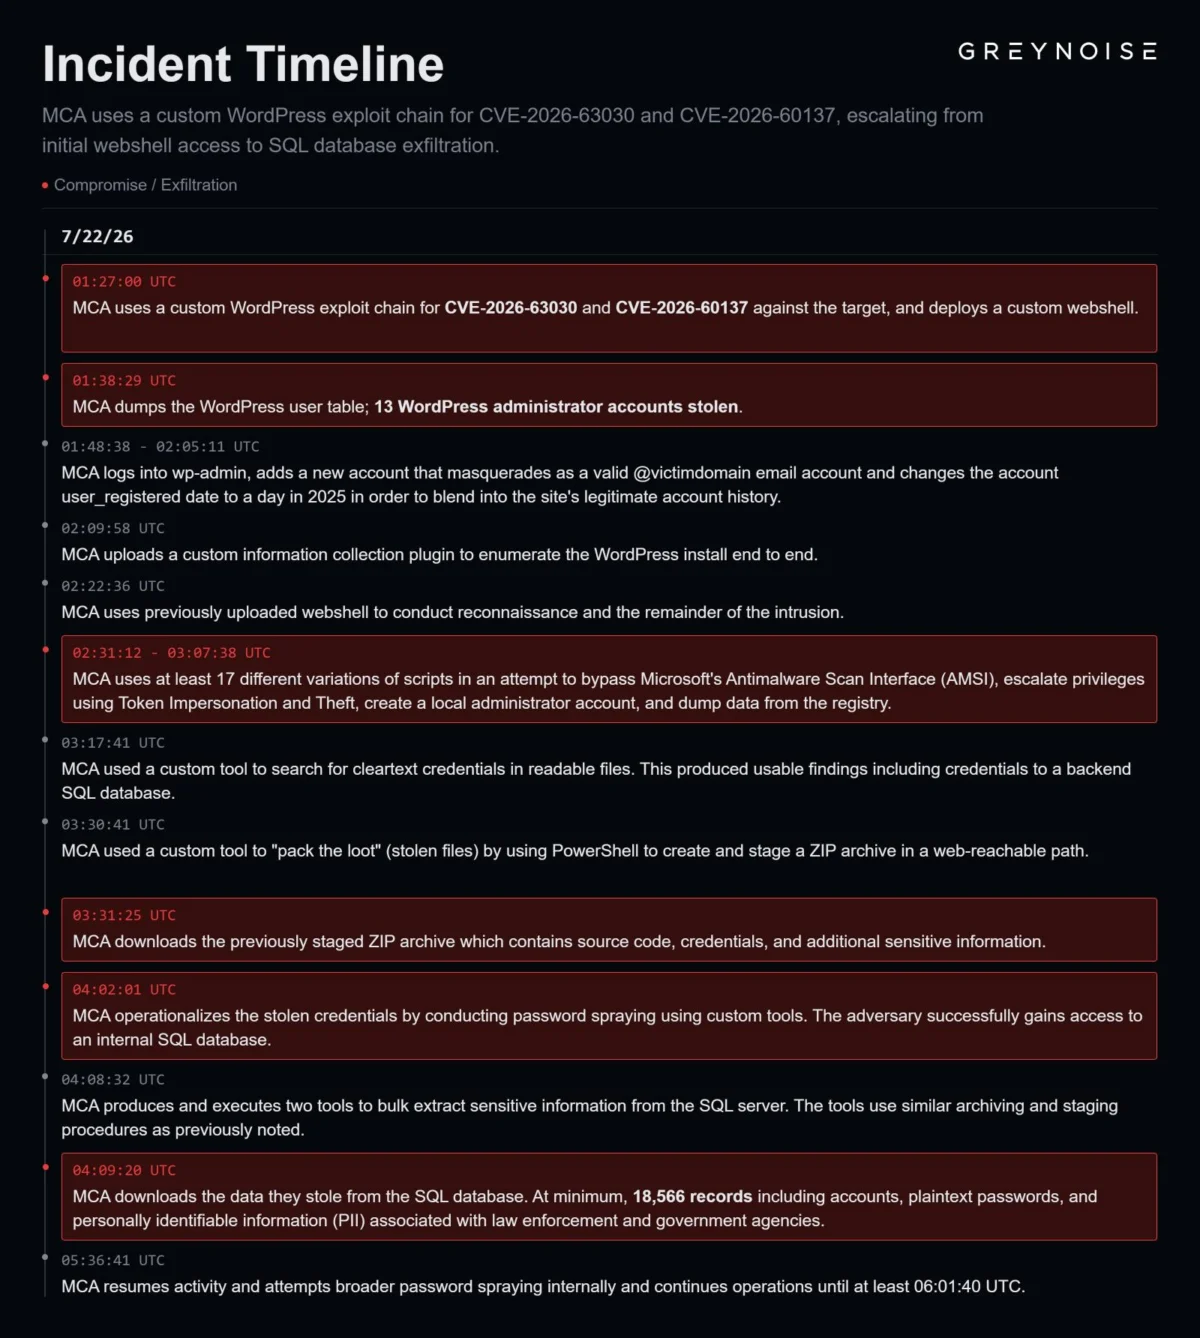
A prominent provider of secure file transfer and communication solutions, Kiteworks, has disseminated an urgent directive to its extensive worldwide customer base, recommending a temporary, six-hour server shutdown this weekend. This unprecedented measure comes in direct response to highly credible threat intelligence received from law enforcement agencies, signaling a potentially imminent and sophisticated cyberattack, which may leverage an undisclosed, critical vulnerability.
The Context of Secure File Transfer and Its Vulnerability
Kiteworks operates at the critical juncture of enterprise data management, offering robust platforms for secure content collaboration, managed file transfer (MFT), and secure email. Its clientele spans highly sensitive sectors, including governmental organizations, major financial institutions, and large enterprises across various industries. These entities rely on Kiteworks’ infrastructure to facilitate the secure exchange of proprietary, confidential, and often regulatory-sensitive information. The very nature of these operations – handling vast volumes of high-value data – positions such platforms as prime targets for a diverse array of malicious actors, ranging from financially motivated cybercriminal syndicates to state-sponsored advanced persistent threat (APT) groups. The compromise of a secure file transfer system can lead to catastrophic data breaches, intellectual property theft, espionage, or disruptive ransomware attacks, making the integrity of these systems paramount.
Understanding the Zero-Day Threat
The core concern underpinning Kiteworks’ extraordinary recommendation appears to be the potential for a "zero-day" attack. A zero-day vulnerability refers to a software flaw that is unknown to the vendor (and thus unpatched) at the time it is discovered and exploited by attackers. The "zero-day" refers to the fact that the developer has had zero days to fix it. Such vulnerabilities are particularly dangerous because there are no immediate defenses or patches available, leaving systems exposed until a fix can be developed and deployed.
The lifecycle of a zero-day exploit typically involves:
- Discovery: A malicious actor (or sometimes a benevolent researcher) identifies a previously unknown flaw in software.
- Exploitation: The attacker develops code, known as an exploit, to leverage this flaw to gain unauthorized access, execute arbitrary code, or disrupt services.
- Deployment: The exploit is then used against target systems.
- Disclosure (or not): The vulnerability may remain undisclosed to the vendor for an extended period, allowing attackers to operate stealthily, or it might be responsibly disclosed, triggering a race to patch.
In the context of Kiteworks’ warning, the implication is that threat intelligence suggests an attacker may possess a functional exploit for an unpatched vulnerability within their system, poised for immediate deployment. The sheer difficulty in defending against a zero-day without prior knowledge necessitates extreme, pre-emptive measures.
An Unprecedented Precautionary Measure
The directive for a global, pre-emptive server shutdown is an exceptionally rare and significant event in the cybersecurity landscape. It underscores the severity of the intelligence received and the potential impact of the anticipated attack. Typically, cybersecurity advisories recommend immediate patching, configuration changes, or enhanced monitoring. A complete system shutdown, even for a limited duration, signifies a belief that conventional defenses may be insufficient against the specific threat identified.
Kiteworks’ communication to its customers, reportedly conveyed by its Chief Information Security Officer and subsequently confirmed through various channels, emphasized the "credible threat intelligence from law enforcement" indicating an imminent attack. This level of collaboration and information sharing between federal authorities and private sector entities highlights the escalating sophistication of cyber threats and the necessity for coordinated defensive strategies. The decision to advise a shutdown, rather than waiting for a confirmed breach or the development of an emergency patch, reflects an abundance of caution and a proactive stance aimed at minimizing potential exposure and damage. It suggests that the intelligence may have been specific enough regarding the nature of the attack, its timing, or the vulnerability involved, to warrant such a drastic, protective maneuver.

Operational Challenges and Global Coordination
Implementing a six-hour global server shutdown presents substantial logistical and operational challenges for Kiteworks’ diverse customer base. With clients spanning all major international time zones – from the Pacific Rim to Europe and the Americas – the recommended shutdown window had to be carefully orchestrated to provide adequate coverage. For instance, customers in Central Europe were advised to power down systems during early morning hours, while those in North America faced late-night Friday or early morning Saturday disruptions.
The recommendation to take systems offline even if they are not directly accessible from the internet further illustrates the breadth of the perceived threat. This implies that the potential attack vector might not solely rely on external network exposure but could involve supply chain compromises, lateral movement within already breached networks, or other sophisticated infiltration techniques that could eventually reach internal systems. For many organizations, shutting down critical file transfer infrastructure, even for a few hours, can disrupt business operations, internal communications, and time-sensitive data exchanges, highlighting the gravity of the situation. This underscores the need for robust incident response plans that can accommodate such pre-emptive, vendor-mandated disruptions.
The Broader Implications for Cybersecurity
This event carries significant implications beyond Kiteworks and its immediate customers. It serves as a stark reminder of the evolving and increasingly aggressive nature of cyber threats. The willingness of a major vendor to recommend a complete system shutdown sets a precedent for how organizations might respond to high-fidelity, pre-attack intelligence in the future.
- Proactive Defense Shift: This incident emphasizes a shift towards more proactive and even disruptive defensive measures when facing severe, intelligence-backed threats. The traditional reactive model of patching after exploitation is increasingly insufficient.
- Intelligence Sharing Imperative: The reliance on "federal intelligence authorities" highlights the critical role of government-private sector intelligence sharing in modern cybersecurity. Effective threat intelligence, when actionable and timely, can enable organizations to pre-emptively mitigate risks.
- Resilience and Business Continuity: For affected organizations, the shutdown period tests their business continuity and disaster recovery plans. It forces a re-evaluation of dependencies on critical infrastructure and the ability to operate, even temporarily, without core services.
- Industry-Wide Scrutiny: This event will likely prompt other providers of secure file transfer and similar critical enterprise software to review their own threat intelligence protocols, incident response plans, and communication strategies with customers.
The Evolving Threat Actor Landscape
While Kiteworks has not publicly attributed the potential attack to a specific threat actor, the pattern of targeting secure file transfer solutions for data theft and extortion is well-established. Sophisticated cybercriminal syndicates and state-sponsored groups frequently leverage zero-day vulnerabilities or newly discovered flaws in widely used enterprise software to achieve their objectives. These actors often conduct extensive reconnaissance, develop bespoke exploits, and launch highly coordinated campaigns designed to maximize impact and financial gain or strategic advantage.
Managed File Transfer (MFT) systems, in particular, have been a recurring target for such groups due to the inherent value of the data they process and store. Successful breaches of MFT platforms can yield vast troves of sensitive corporate, customer, and government data, which can then be used for extortion, intellectual property theft, competitive advantage, or intelligence gathering. The financial incentives for such attacks are immense, and the resources dedicated by these sophisticated adversaries are considerable, necessitating an equally sophisticated and vigilant defensive posture.
Future Outlook and Recommendations
The Kiteworks advisory serves as a potent reminder for all organizations regarding the necessity of a multi-layered cybersecurity strategy:
- Vigilant Threat Intelligence Integration: Organizations must actively seek out and integrate threat intelligence from various sources, including government agencies, industry-specific information sharing and analysis centers (ISACs), and commercial intelligence providers.
- Robust Patch Management and Version Control: While a zero-day by definition is unpatched, maintaining all systems on the latest, fully patched versions (as Kiteworks explicitly recommends for its 9.5.1 release) significantly reduces the attack surface from known vulnerabilities.
- Comprehensive Incident Response Planning: Develop and regularly test incident response plans that include scenarios involving pre-emptive shutdowns or vendor-mandated disruptions. This ensures business continuity and a swift, organized reaction.
- Network Segmentation and Least Privilege: Implement strict network segmentation to limit the lateral movement of attackers within a network, even if an initial compromise occurs. Enforce the principle of least privilege for all user accounts and system access.
- Proactive Monitoring and Anomaly Detection: Deploy advanced security monitoring tools, including Endpoint Detection and Response (EDR) and Security Information and Event Management (SIEM) systems, to detect anomalous behavior that could signal an attempted or successful intrusion.
- Supply Chain Security Audits: Regularly audit the security posture of third-party vendors and supply chain partners, especially those providing critical software or services.
The decision by Kiteworks to issue such an extraordinary warning underscores the dynamic and perilous nature of the modern cyber threat landscape. It highlights the critical balance between maintaining operational availability and implementing necessary security measures to safeguard invaluable digital assets. As cyber adversaries continue to evolve their tactics and capabilities, the collaboration between intelligence agencies and the private sector, coupled with unprecedented proactive defensive strategies, will become increasingly vital in protecting global digital infrastructure.

 Lisa Mariana
 Aura Kasih