 Safa Marwah
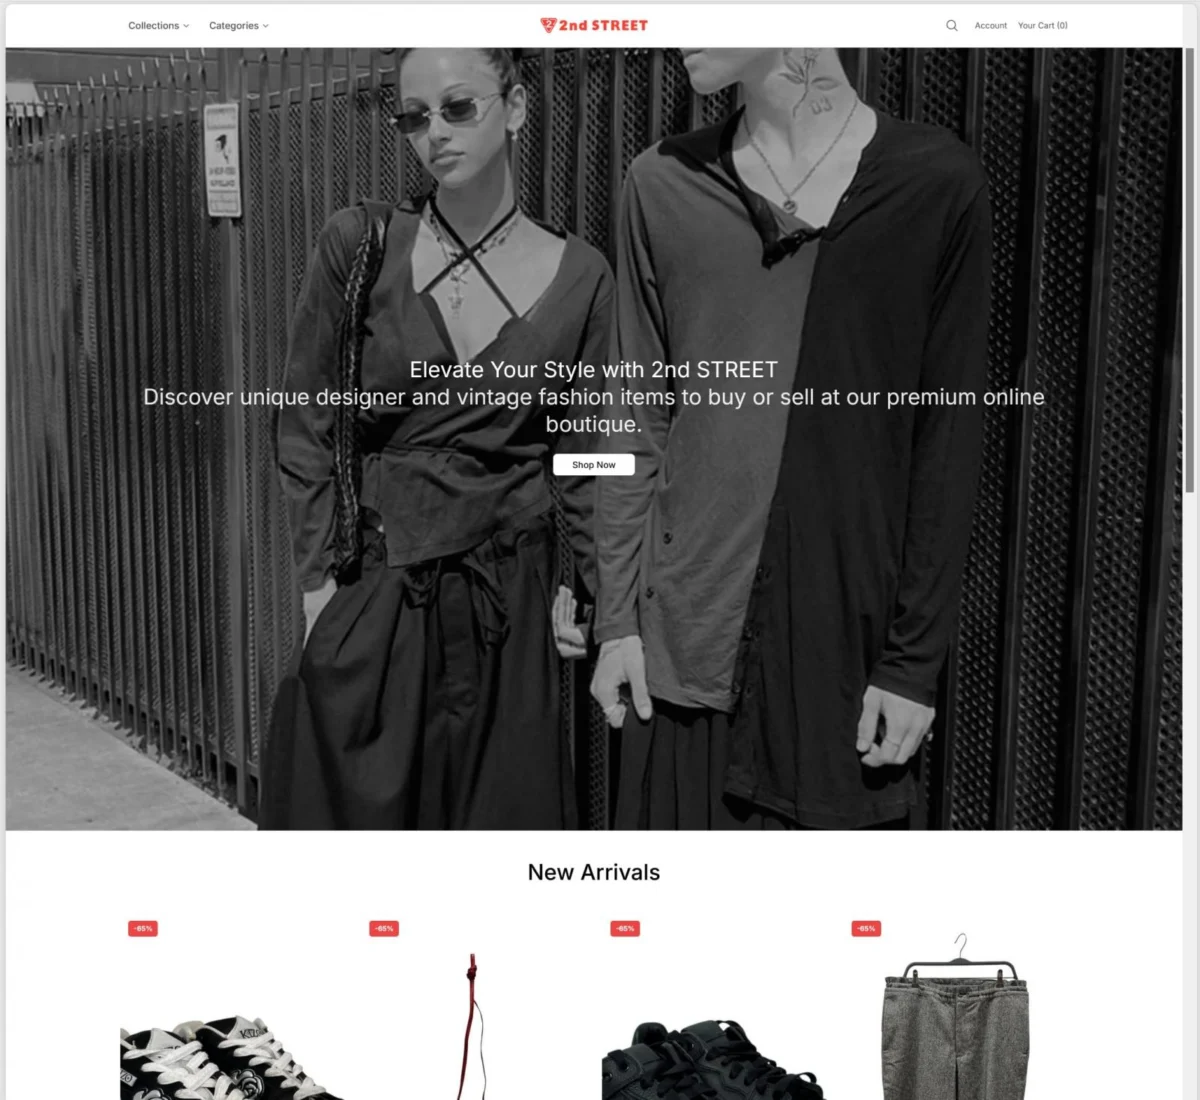
A sophisticated global cybercrime syndicate, identified as "DoppelCart," has unleashed an unprecedented digital infrastructure comprising over 119,000 fraudulent online storefronts meticulously designed to illicitly acquire payment card information and infringe upon intellectual property rights. This sprawling network represents a significant escalation in e-commerce fraud, demonstrating advanced operational coordination and a systematic approach to consumer deception.
Magnitude and Operational Scale
The sheer scale of the DoppelCart operation is without precedent in documented cybercrime history. With over 119,000 distinct domains, this syndicate has established an infrastructure that dwarfs previous large-scale fraudulent networks. A significant proportion of these malicious domains are registered under the .SHOP top-level domain (TLD), representing an alarming 2.72% of all active websites within that specific TLD ecosystem. This concentration within a commercially oriented TLD highlights a strategic choice by the perpetrators, likely driven by the perceived legitimacy and availability of domain names relevant to retail operations. The proliferation within .SHOP domains also poses a particular challenge for the TLD registry and registrars, who face the complex task of identifying and mitigating such widespread abuse while maintaining the integrity of their domain space.
In-depth investigations by a prominent European cybersecurity research entity have brought to light the intricate workings of this extensive fraud network. This operation now stands as the most expansive documented cluster of fraudulent e-commerce platforms, dwarfing previous high-profile cases such as "BogusBazaar," which managed approximately 75,000 illicit sites and was implicated in an estimated 850,000 fraudulent transactions. The fact that over 105,000 of these deceptive digital outlets remain operational underscores the persistent and pervasive nature of the threat, continuing to expose consumers globally to financial exploitation. The magnitude of this network suggests a highly automated and well-resourced criminal enterprise, capable of rapidly deploying and maintaining a vast number of seemingly legitimate online presences.
Technical Underpinnings and Infrastructure
Detailed technical analysis reveals a remarkable uniformity across the DoppelCart network, indicating a highly centralized and efficiently managed operation. An estimated 96% of the confirmed fraudulent sites utilize identical core build files, suggesting a standardized deployment mechanism and a modular approach to storefront creation. This uniformity simplifies management for the perpetrators, allowing for rapid replication and deployment across thousands of domains. Furthermore, these sites route their operations through a consolidated infrastructure of just 27 distinct commerce backend systems. Such consolidation points to a sophisticated architecture designed for efficiency, centralized data collection, and resilience against takedown attempts. While appearing disparate to the casual observer, the underlying infrastructure is tightly integrated, enabling coordinated malicious activity.
The method of data exfiltration employed by DoppelCart demonstrates a clear understanding of modern web communication protocols. Forensic examination of numerous checkout interfaces within the operational cluster has uncovered embedded malicious code designed for the surreptitious collection of sensitive financial and personal data. This includes, but is not limited to, credit card numbers, expiration dates, card verification values (CVV), cardholder names, billing addresses, email addresses, and phone numbers. Crucially, this exfiltrated data, encompassing every input field, is immediately transmitted in real-time via WebSockets to the syndicate’s sophisticated command-and-control (C2) infrastructure. The use of WebSockets, a persistent connection protocol, ensures rapid and efficient data transfer, minimizing the window for detection and maximizing the speed at which stolen information can be leveraged by the attackers.
A particularly advanced feature observed in the malicious scripts is their capability to intercept and relay one-time confirmation codes (OTPs) issued by financial institutions. This functionality enables the fraudsters to circumvent multi-factor authentication (MFA) protocols, which are increasingly relied upon as a critical security layer for online transactions. By intercepting OTPs, the attackers can authorize fraudulent purchases, effectively bypassing one of the strongest defenses against credit card theft. This level of sophistication highlights a well-resourced and technically adept criminal group, moving beyond simple card skimming to actively subvert enhanced security measures.
Deception Tactics and Brand Impersonation
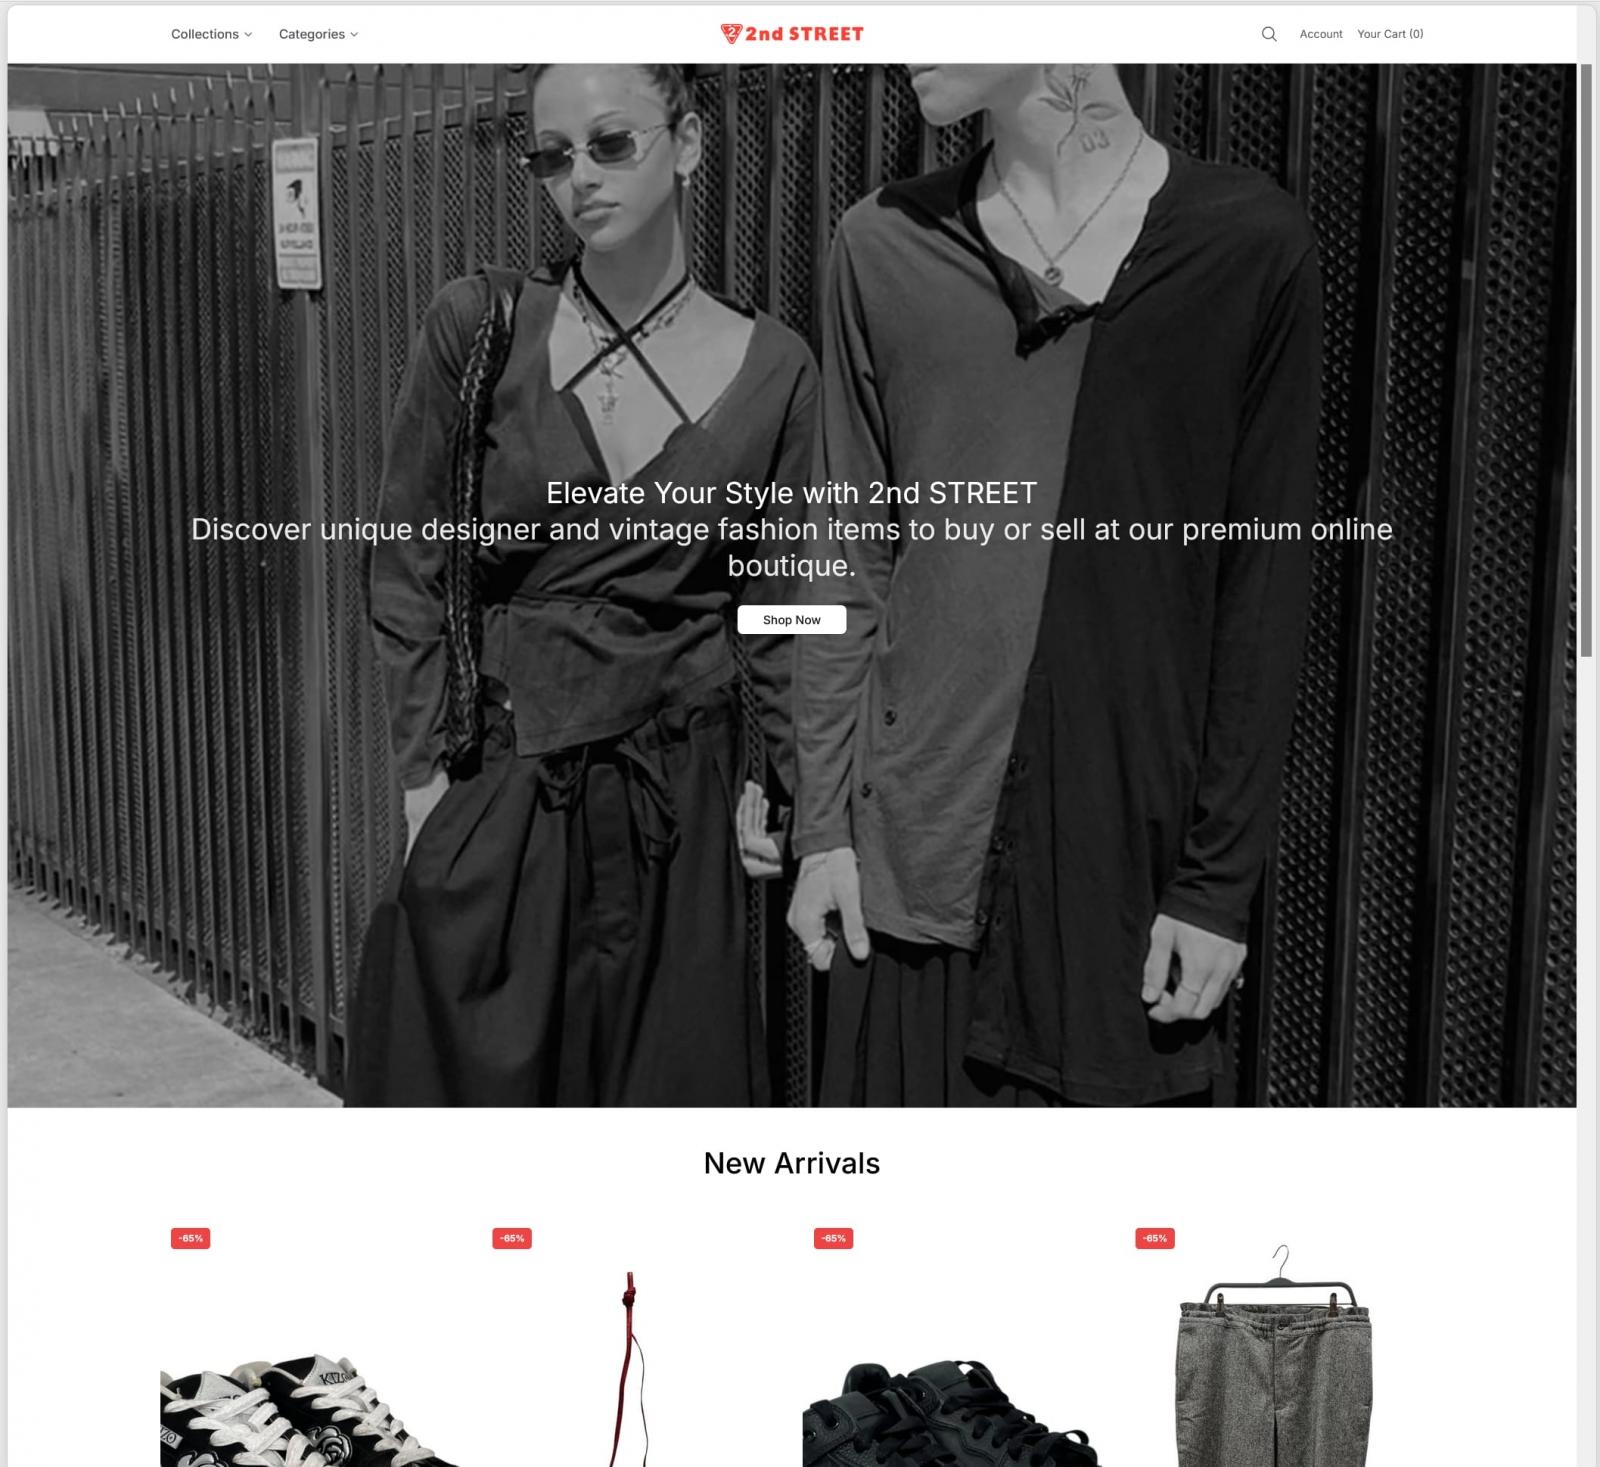
The deceptive strategy employed by DoppelCart involves meticulous impersonation of established, reputable businesses. These fraudulent platforms meticulously replicate genuine product catalogs, descriptive content, brand imagery, and corporate identities. In some instances, assets such as product photos and logos are directly loaded from the legitimate companies’ own servers. This practice not only enhances the perceived authenticity of the fake sites but also makes them more challenging for automated detection systems to differentiate from their genuine counterparts, as they borrow elements from trusted sources.
The syndicate’s targets span an extensive range of 44,182 distinct brands, typically featuring a median of two cloned instances per brand. This broad targeting strategy suggests an opportunistic approach, aiming to cast a wide net across various consumer markets. However, certain high-value or popular brands, including but not limited to SodaStream, Velasca, CurrentBody, Daniel Wellington, Dreame, Horze, MOVA, and SPARK PAWS, have been subjected to more aggressive cloning, with some enduring over 30 dedicated fraudulent storefronts. This concentrated targeting of specific brands likely reflects their market popularity, high average transaction values, or consumer loyalty, making them attractive targets for exploitation.
A primary tactic for enticing unsuspecting consumers involves advertising substantial discounts, frequently reaching up to 65% off retail prices. This strategy preys on the prevalent consumer desire for advantageous deals, especially in an economically sensitive environment. The allure of "too good to be true" offers often overrides critical judgment, leading shoppers to overlook subtle indicators of fraud. The perceived urgency created by such discounts further pressures consumers into hasty purchases, reducing the likelihood of thorough vetting of the website’s legitimacy.
A particularly insidious element of the deception involves the inclusion of the legitimate support contact details of the impersonated brands on some fraudulent storefronts. This tactic diverts victim complaints and inquiries regarding undelivered purchases directly to the unsuspecting legitimate businesses. This not only burdens the genuine companies with fraudulent customer service issues but also damages their brand reputation, as consumers mistakenly attribute the fraudulent experience to the authentic brand. This secondary layer of impact amplifies the harm beyond direct financial loss to the victims.
Impact and Implications
The ramifications of the DoppelCart operation are far-reaching, affecting consumers, legitimate businesses, financial institutions, and the broader digital economy.
- For Consumers: Victims face direct financial losses from unauthorized transactions, the potential for identity theft due to compromised personal information, and the arduous process of dispute resolution with banks and credit card companies. Beyond monetary costs, there is a significant erosion of trust in online shopping, leading to heightened anxiety and reluctance to engage in e-commerce.
- For Legitimate Businesses: Brands targeted by DoppelCart suffer severe reputational damage, as their names become associated with fraudulent activity. This can lead to decreased sales, customer churn, and increased costs related to handling misdirected customer service inquiries and legal efforts to protect their intellectual property. The unauthorized use of their content and branding also constitutes a direct violation of copyright and trademark laws.
- For Financial Institutions: Banks and credit card companies incur substantial costs associated with fraud detection, investigation, chargebacks, and reimbursing affected customers. The sophisticated nature of DoppelCart, particularly its ability to bypass OTPs, places additional strain on existing fraud prevention systems and necessitates continuous investment in advanced security measures.
- For the Cybersecurity Landscape: The DoppelCart operation highlights critical vulnerabilities within the e-commerce ecosystem, including weaknesses in domain registration processes, the challenges of proactive brand protection, and the need for more robust collaborative frameworks for information sharing and takedown initiatives. The lack of response from certain hosting providers, as reported by the investigating cybersecurity firm, underscores systemic challenges in holding infrastructure providers accountable for abuse on their networks.
Mitigation and Prevention Strategies
Addressing a threat of this magnitude requires a multi-faceted approach involving various stakeholders:
- For Consumers: Education remains paramount. Shoppers must be vigilant, scrutinizing URLs for anomalies, verifying website legitimacy through independent reviews or direct contact with the brand, and exercising caution with offers that appear excessively generous. Using strong, unique passwords and enabling multi-factor authentication on all online accounts are critical personal security measures.
- For Businesses: Proactive brand monitoring and domain surveillance are essential to detect instances of impersonation and domain squatting. Implementing rapid takedown procedures in collaboration with registrars and hosting providers is crucial. Furthermore, clear communication channels for customers to report suspected fake sites can help mitigate reputational damage and facilitate faster action. Collaborative efforts with cybersecurity firms specializing in brand protection and intelligence sharing are increasingly vital.
- For Financial Institutions: Continuous enhancement of fraud detection algorithms, particularly those capable of identifying real-time anomalies in transaction patterns, is necessary. Strengthening authentication protocols and exploring innovative biometric or behavioral authentication methods can provide additional layers of security against sophisticated attacks like OTP interception.
- For Domain Registries and Registrars: More stringent vetting processes for domain registrations, alongside automated systems for detecting suspicious registration patterns and high-volume abuse reports, are imperative. Expedited procedures for suspending or revoking domains found to be engaged in fraudulent activities are also critical. Industry-wide collaboration and adherence to best practices for abuse handling are fundamental to curbing such widespread exploitation.
Future Outlook and Challenges
The DoppelCart operation serves as a stark reminder of the evolving and escalating nature of cybercrime in the digital age. The increasing sophistication, automation, and global reach of such syndicates present persistent challenges for law enforcement, cybersecurity professionals, and the wider internet governance community. The use of advanced techniques like real-time data exfiltration via WebSockets and OTP bypass mechanisms signals a trend towards more complex and adaptive fraud schemes.
The sheer volume of domains involved also highlights the economic incentives for these criminal enterprises, driven by the low cost of domain registration and hosting combined with the potential for substantial illicit gains. Combating such large-scale, cross-border operations necessitates enhanced international cooperation, harmonized legal frameworks, and intelligence sharing between private sector entities and governmental agencies. The future battle against e-commerce fraud will likely involve a continuous arms race between sophisticated attackers leveraging artificial intelligence and machine learning for automation and defenders deploying similar technologies for detection and prevention. The ultimate success in mitigating these threats will depend on a collective and coordinated effort to secure the digital ecosystem from end to end.

 Lisa Mariana
 Aura Kasih
 Ayu Aulia