Safa Marwah
- Cybersecurity
- September 25, 2026
- 99 views
Global Cybersecurity Alert: Kiteworks Issues Urgent Six-Hour Server Deactivation Directive Amidst Imminent Zero-Day Threat Intelligence
A prominent provider of secure file transfer and communication solutions, Kiteworks, has disseminated an urgent directive to its extensive worldwide customer base, recommending a temporary, six-hour server shutdown this weekend.…
- Cybersecurity
- September 25, 2026
- 112 views
Digital Asset Exchange Bitget Suffers $351.6 Million Heist, North Korean Cybercriminals Suspected
A sophisticated cyberattack has resulted in the expropriation of approximately $351.6 million from the operational "hot" and "warm" digital asset wallets of Bitget, a prominent cryptocurrency exchange, with initial forensic…
- Cybersecurity
- September 22, 2026
- 125 views
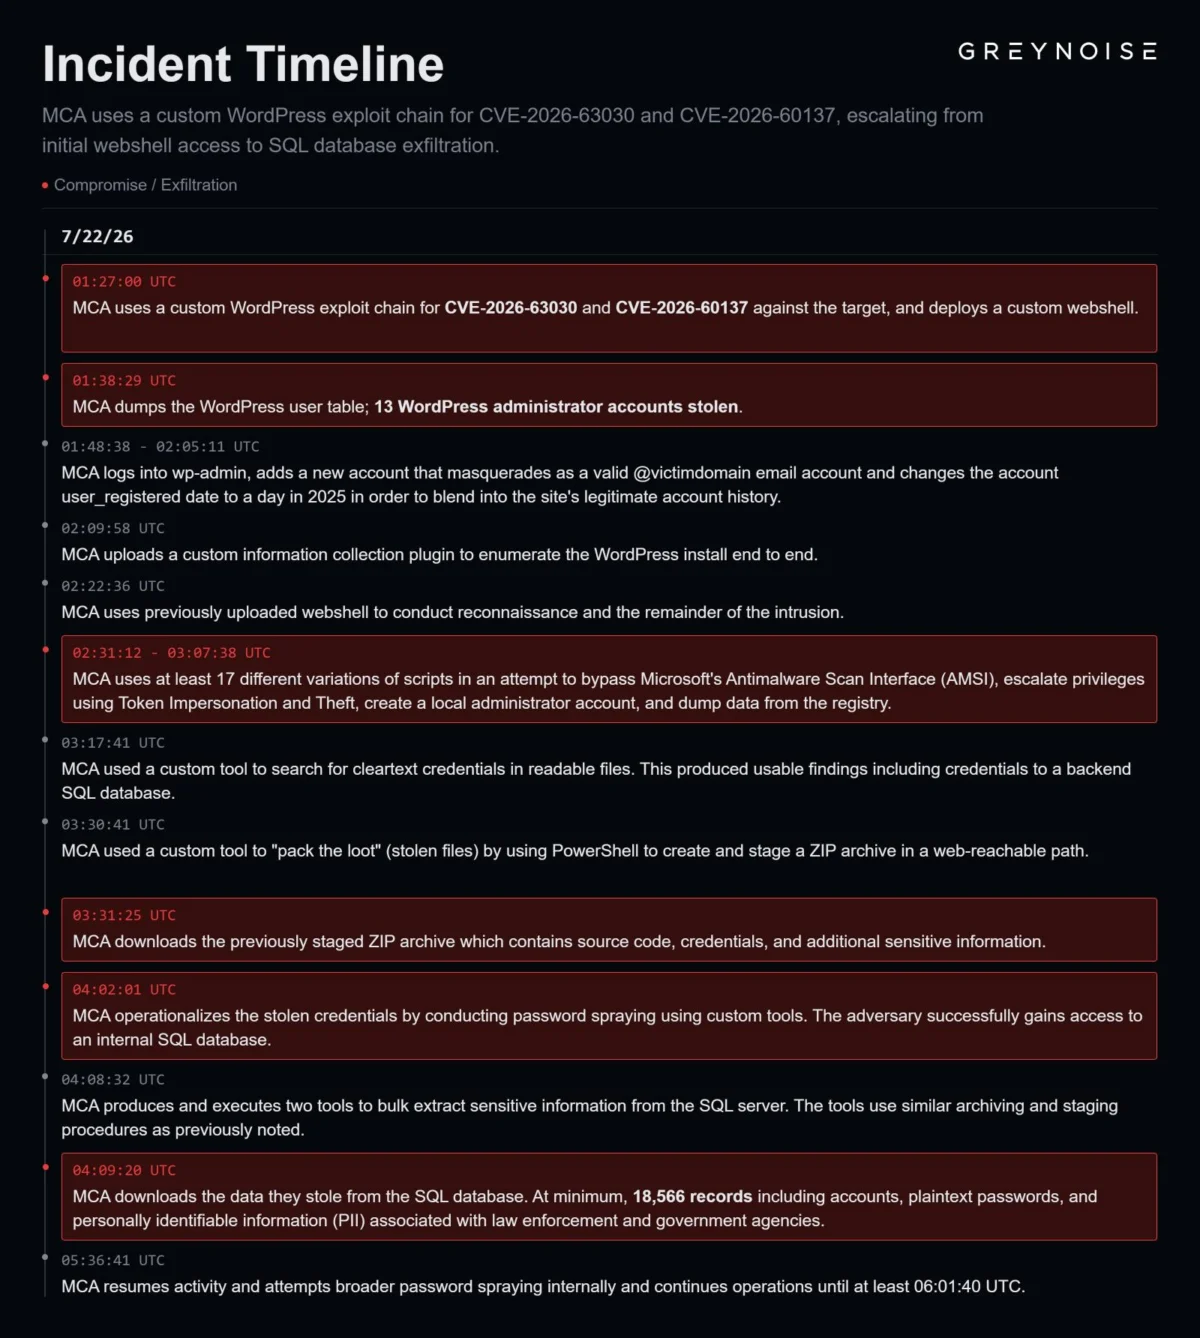
Chinese hackers exploit WordPress, Zyxel flaws to steal govt data
A sophisticated, state-sponsored cyber espionage group, believed to originate from China, has been observed conducting an extensive campaign exploiting a diverse array of software and hardware vulnerabilities, including critical flaws…
- Cybersecurity
- September 21, 2026
- 134 views
Urgent Directive Issued as CISA Flags Actively Exploited Critical Linux Kernel Vulnerabilities
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has issued a high-priority alert, warning organizations about the immediate and active exploitation of three distinct vulnerabilities within the Linux kernel, one…
- Cybersecurity
- September 21, 2026
- 210 views
Cloud Commerce Platform BigCommerce Grapples with Supply Chain Breach Via Compromised Third-Party Application Credentials
Leading cloud-based e-commerce provider BigCommerce has initiated notifications to numerous merchants regarding a significant data incident stemming from the compromise of credentials associated with Ribon, a third-party application, which attackers…
- Cybersecurity
- September 20, 2026
- 124 views
Evolving Threat Landscape: Malicious npm Packages Execute Covert Operations by Evading Install-Time Defenses Through Runtime Subterfuge
A recent and extensive malicious campaign targeting the widely used npm ecosystem represents a significant advancement in software supply chain attacks, as threat actors increasingly circumvent established install-time security measures…
- Cybersecurity
- September 19, 2026
- 118 views
Unprecedented Global Infiltration: North Korea’s WaterPlum Group Exploits Job Seekers, Stealing Millions for State Programs
An unprecedented multinational security alert has detailed a sophisticated and far-reaching cyber espionage and financial illicit operation orchestrated by the North Korean state-sponsored group known as WaterPlum, revealing the compromise…
- Cybersecurity
- September 19, 2026
- 189 views
Exploiting Integrated AI: A Novel Attack Vector Subverts Browser Agents Through Malicious Extensions
A significant new security vulnerability has emerged, demonstrating how malevolent browser extensions can commandeer the built-in artificial intelligence assistants within leading web browsers, potentially compromising sensitive user data and executing…
- Cybersecurity
- September 18, 2026
- 145 views
Major Security Compromise at Gyazo Exposes Millions of User Records and Sensitive Content Metadata
A significant security incident has impacted Gyazo, a widely utilized cloud-based screen capture and sharing service, leading to the unauthorized acquisition of approximately 23.6 million user records. This extensive breach,…
- Cybersecurity
- September 17, 2026
- 129 views
Advanced Android Threat RatHat Employs AI for Unprecedented Device Control and Data Harvesting
A novel strain of Android malware, identified as RatHat, has emerged as a significant threat, distinguishing itself through an innovative AI-driven subsystem that facilitates autonomous remote navigation and comprehensive control…
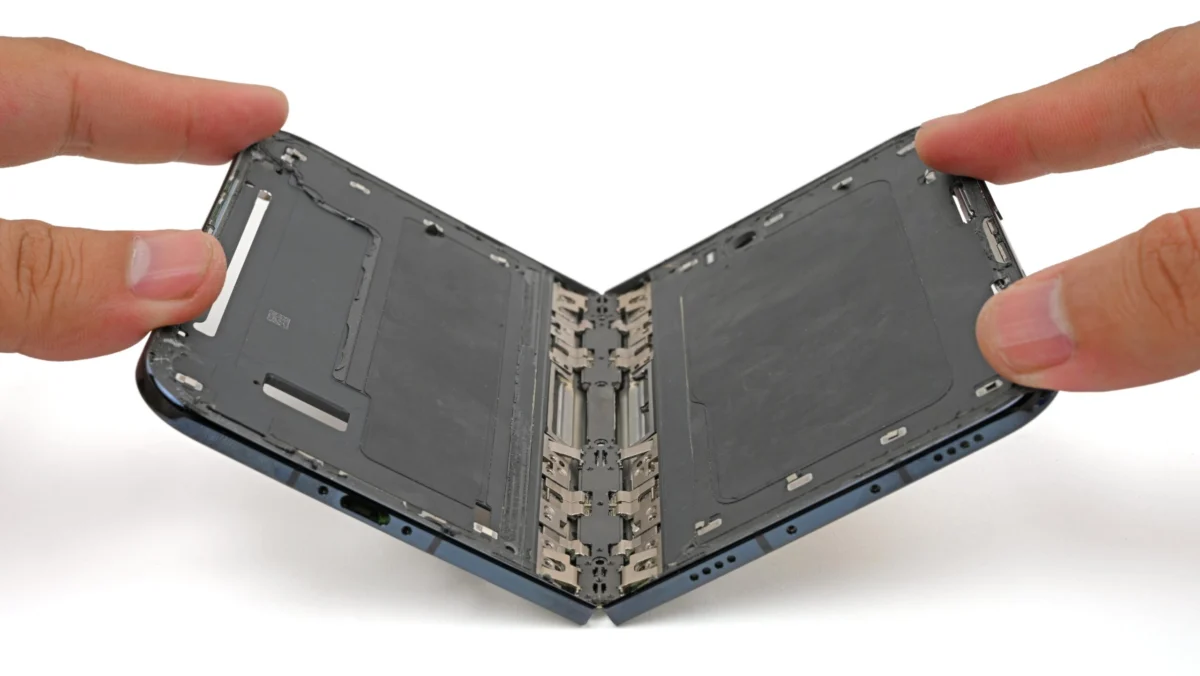
Unfolding Disaster: The iPhone Duo’s Hinge Crisis Threatens Display Integrity
Aura Kasih
- October 27, 2026
- 1 views
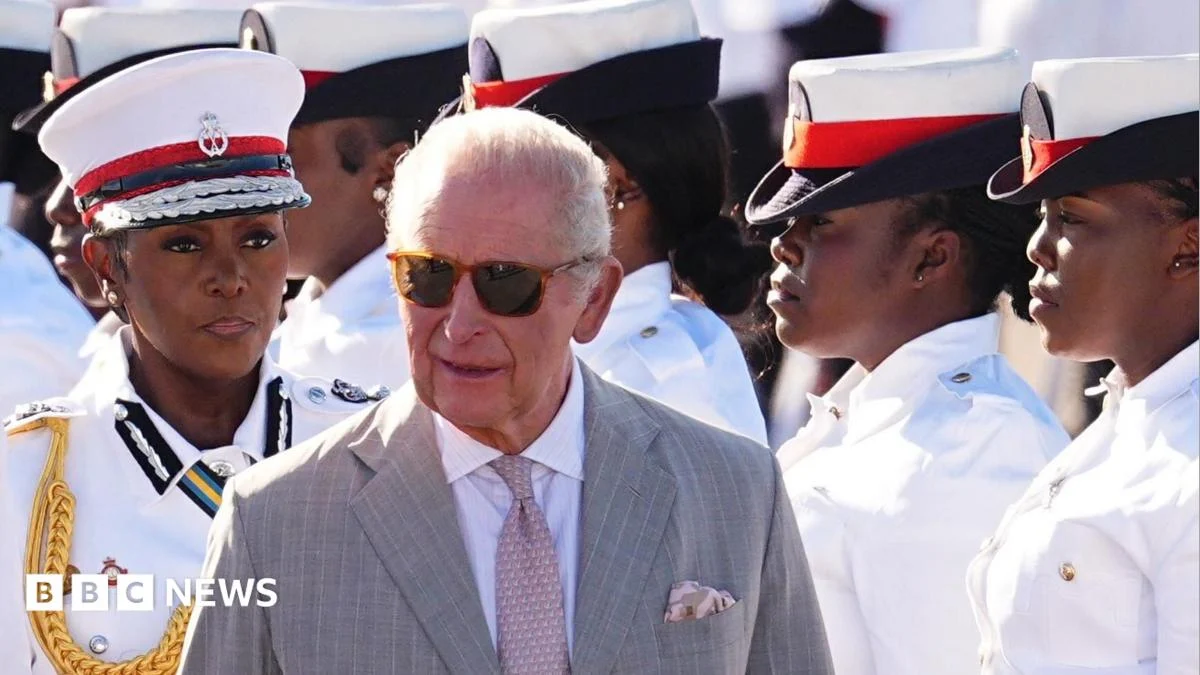
Royal Diplomacy Confronts Colonial Past and Climate Future in Caribbean Tour
Lisa Mariana
- October 27, 2026
- 1 views
Academic Discontent Mounts as AI Research Becomes Increasingly Opaque
- October 27, 2026
- 1 views
Harry Kane Crowned World’s Best: A New Era of Individual Excellence Recognized
- October 26, 2026
- 1 views
