 Safa Marwah
A profound security oversight within a defunct variant of the once-popular Popcorn Time application left an estimated millions of personal computers and enterprise endpoints susceptible to sophisticated remote code execution (RCE) attacks. This widespread vulnerability, stemming from an insecure update mechanism in the Time4Popcorn client, a successor to the original BitTorrent streaming interface, has been proactively mitigated by cybersecurity researchers who remotely neutralized the vulnerable component. Their intervention successfully averted a potential large-scale compromise, preventing malicious actors from exploiting the flaw to gain unauthorized control over countless systems.
The revelation underscores the pervasive and enduring risks associated with orphaned software and neglected digital infrastructure. Researchers at Eye Security identified the critical flaw, designated as CVE-2026-30612, which specifically affected the update functionality for both Windows and macOS installations. The core of the problem lay in the application’s reliance on an unencrypted HTTP connection to an abandoned domain, popcorntimeupd.xyz, for fetching updates, coupled with a complete absence of digital signature verification for downloaded executables. This combination created a gaping security chasm, allowing any entity that could control or intercept traffic to the update domain to inject and execute arbitrary code with elevated privileges—specifically, SYSTEM-level access on Windows machines and root access on macOS systems.
Popcorn Time initially gained notoriety for its user-friendly, Netflix-esque interface that streamlined the consumption of pirated content via BitTorrent streaming. While the original project faced significant legal challenges leading to its cessation, numerous independent forks, such as Time4Popcorn, swiftly emerged, capitalizing on the established brand and attracting a vast user base. These derivative applications, despite their legal ambiguities, continued to operate, often with minimal security scrutiny, perpetuating a cycle of risk for their users.
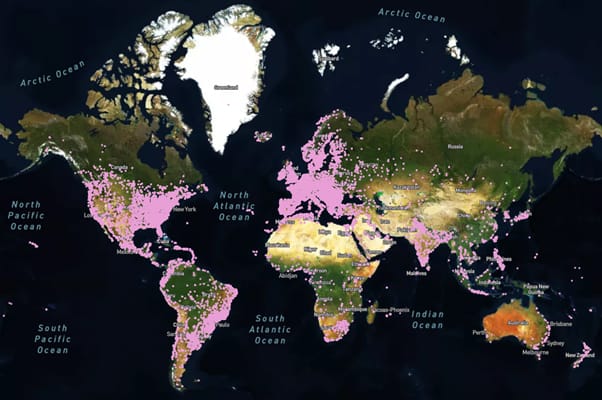
Eye Security’s investigation commenced with the strategic acquisition of the popcorntimeupd.xyz domain, which had been left unregistered after the original developers abandoned the project. Upon gaining control, the security firm meticulously monitored incoming connections, observing a staggering volume of requests. Their telemetry indicated approximately 3 million distinct Windows clients and 350,000 macOS clients attempting to contact the defunct update server. This discovery illuminated the immense scale of potential exposure, revealing a digital landscape littered with dormant yet vulnerable applications.
The geographical distribution of these connections was equally concerning, originating from a diverse array of networks including residential internet service providers, corporate environments, governmental institutions, and even military installations. Intriguingly, subsequent analysis suggested that a significant portion of these systems were not actively utilizing the Time4Popcorn application. Instead, the software appeared to have been installed at some point and then largely forgotten, left to languish as a silent, ticking time bomb within the digital ecosystem. This phenomenon highlights a common user habit: installing software for a specific, often temporary, purpose and then neglecting its removal or maintenance, thereby creating latent attack vectors.
The gravity of the situation was immediately apparent to the researchers. The potential for a malicious entity to commandeer such a vast network of compromised devices was immense. As articulated by Eye Security, the ability to deliver arbitrary code with elevated privileges across millions of systems presented a severe threat, capable of manifesting into a colossal botnet, a platform for widespread data exfiltration, or a launchpad for sophisticated ransomware attacks. The implications for national security, corporate integrity, and individual privacy were profound, necessitating urgent and decisive action.
Following their initial findings, the researchers expanded their defensive posture by registering an additional 14 domains historically associated with the Time4Popcorn service, thereby consolidating control over potential attack surfaces. This proactive measure was a critical step in preventing other malicious actors from acquiring these domains and weaponizing them against the unsuspecting user base.
The subsequent phase of Eye Security’s operation, termed "Operation Ixim," involved a meticulously planned and executed remediation effort. Between November 2025 and March 2026, the firm leveraged the very vulnerability they had uncovered to deliver a benign payload designed to neutralize the insecure update mechanism. This remediation code was engineered to stop and permanently disable the Time4Popcorn updater service on affected Windows and macOS machines. Crucially, the payload was designed with stringent ethical and legal boundaries: it collected no host data or telemetry, nor did it delete any existing files from users’ systems. This cautious approach ensured that the intervention remained within a fully legal and ethical framework, focusing solely on mitigating the security risk without infringing on user privacy or data integrity.
The implementation of Operation Ixim was not without its challenges. During the testing phase, the research team encountered instances where their benign payload, despite its defensive purpose, was flagged by various antivirus products for attempting to disable a system service. This necessitated iterative modifications to the payload to circumvent these security measures, highlighting the delicate balance between proactive defense and the heuristics of endpoint protection software.
Despite these hurdles, the remediation proved highly effective. Following the broad deployment of their fix, Eye Security recorded over 2 million successful update downloads. By March 1 of the current year, requests to the controlled update domains had plummeted by a remarkable 98%, signaling the near-complete neutralization of the vulnerability across the affected Windows and macOS client base. This dramatic reduction in update requests served as a clear indicator of the successful disabling of the insecure updater service on a massive scale.
Upon the successful conclusion of Operation Ixim, Eye Security responsibly transferred ownership of the critical domains to The Shadowserver Foundation, a non-profit organization dedicated to improving global internet security. This handover ensures that these domains remain under benevolent control, preventing any future attempts by malicious entities to exploit them. The Shadowserver Foundation’s ongoing stewardship provides a crucial layer of long-term protection, cementing the efforts of Eye Security in safeguarding millions of devices.
Despite this significant achievement, the researchers cautioned that the threat landscape is not entirely clear for all users of the Time4Popcorn application. A notable segment of users, specifically those on Android platforms, remains exposed. Due to the inherent architectural differences of mobile operating systems, delivering an update to Android devices typically requires explicit user interaction, a hurdle that prevented Eye Security from remotely disabling the updater on mobile clients. This means Android users who still have the Time4Popcorn app installed are still potentially vulnerable to similar exploits if the underlying update infrastructure for their specific version were to be compromised.
Furthermore, the Time4Popcorn application itself presents additional, inherent security risks. It utilizes a severely outdated Chrome engine, dating back to 2014, which lacks modern sandbox protections. Such an antique browser engine is replete with unpatched vulnerabilities that could be exploited by sophisticated attackers, even without relying on the update mechanism. Simply running the application could expose users to drive-by downloads, browser exploits, and other forms of attack targeting the aged rendering engine.
Given these lingering threats, the unequivocal recommendation for all users of Time4Popcorn, regardless of their operating system, is to immediately and thoroughly remove the software from their systems. This action represents the most effective and direct way to eliminate all associated security risks.
The saga of the abandoned Popcorn Time app serves as a potent case study in the broader challenges of digital security. It underscores several critical lessons for both software developers and end-users. For developers, the paramount importance of implementing robust and secure update mechanisms, including cryptographic verification and encrypted communication protocols (HTTPS), cannot be overstated. This responsibility extends throughout the entire software lifecycle, even into the abandonment phase, where proper decommissioning of infrastructure is crucial. For users, the incident highlights the vital necessity of practicing good digital hygiene: regularly auditing installed applications, promptly uninstalling unused or unknown software, and being critically aware of the provenance and security practices of any application they choose to install. In an increasingly interconnected world, forgotten software can become a silent conduit for significant cyber threats, demanding continuous vigilance and proactive management of one’s digital footprint.

 Aura Kasih
 Lisa Mariana