
Safa Marwah
- Cybersecurity
- August 23, 2026
- 93 views
Peripheral Lighting Systems Implicated in Widespread Windows Gaming Instability Following Recent OS Updates
A series of critical system disruptions, manifesting as game crashes, launch failures, and unexpected reboots, affecting a significant segment of the Windows gaming community, has been tentatively attributed by Microsoft…
- Cybersecurity
- August 23, 2026
- 62 views
Stealthy Android Malware Leverages VPN Spoofing and ADB Automation to Cripple Defenses and Harvest Data
A sophisticated Android malware variant, dubbed "ToxicPanda 2.0," has emerged with alarming new capabilities, marking a significant escalation in mobile threat landscapes. This advanced iteration now exploits virtual private network…
- Cybersecurity
- August 23, 2026
- 47 views
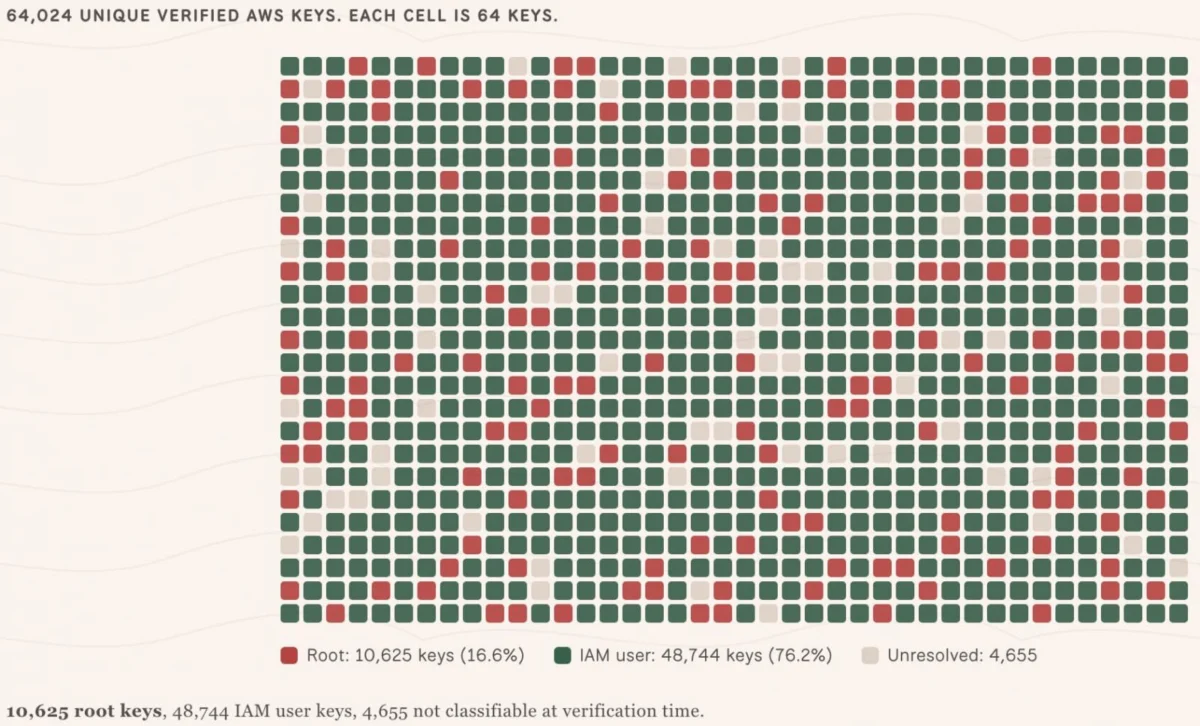
Unrestricted Access: Thousands of Exposed AWS Credentials Grant Attackers Full Corporate Cloud Control
A comprehensive analysis has revealed a staggering number of Amazon Web Services (AWS) access keys, numbering in the thousands, remain publicly exposed and actively functional, presenting a critical vulnerability that…
- Cybersecurity
- August 23, 2026
- 45 views
Emergence of SynkLoader: A Sophisticated Multi-Language Malware Family Exploiting Microsoft Teams for Credential Theft
A previously uncataloged and highly adaptable malware strain, now identified as SynkLoader, has been observed leveraging sophisticated phishing tactics within Microsoft Teams to illicitly acquire user credentials through a meticulously…
- Cybersecurity
- August 22, 2026
- 46 views
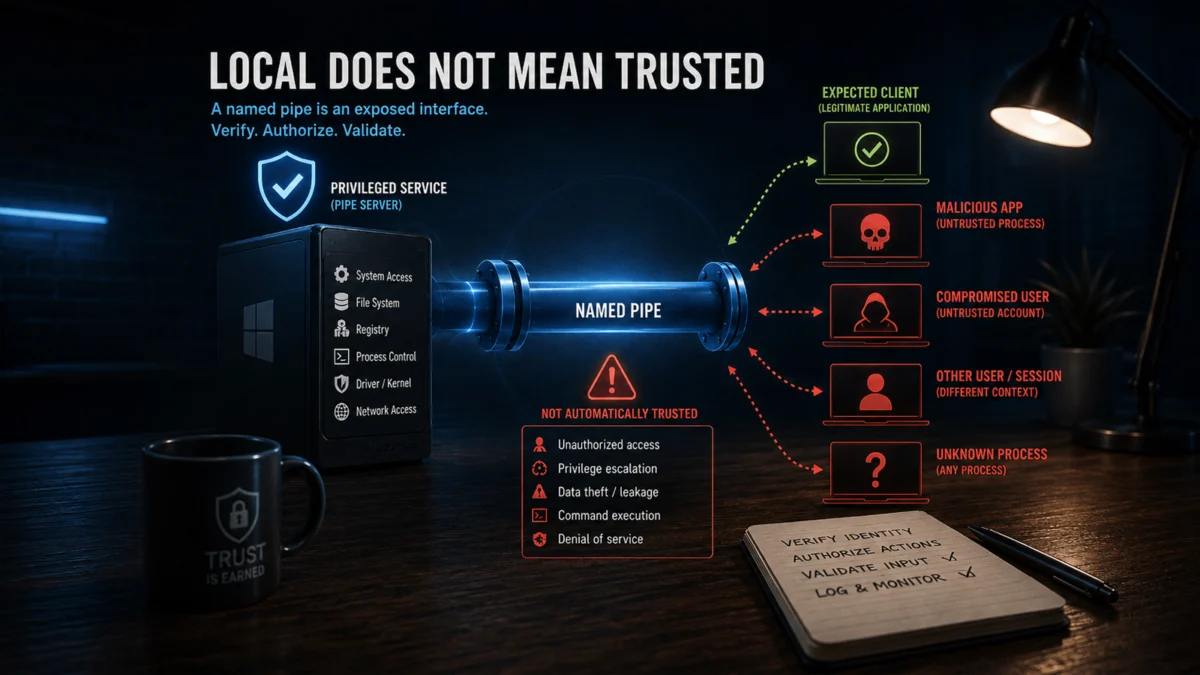
Fortifying Windows Inter-Process Communication: A Comprehensive Analysis of Named Pipe Security Vulnerabilities
Inter-process communication (IPC) mechanisms are fundamental to modern operating systems, enabling diverse applications to interact efficiently. On Windows platforms, named pipes stand out as a widely adopted method for local…
- Cybersecurity
- August 22, 2026
- 72 views
Automotive Infotainment Systems Compromised: A Deep Dive into a Novel Android Botnet and Ad Fraud Scheme
A sophisticated supply-chain attack has been uncovered, leveraging seemingly legitimate device update channels to implant malicious software onto Android-based car head units, subsequently enrolling them into a clandestine proxy botnet…
- Cybersecurity
- August 10, 2026
- 53 views
Critical Progress Kemp LoadMaster Flaw Under Active Attack, CISA Urges Immediate Remediation
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has issued an urgent warning regarding the active exploitation of a severe command injection vulnerability, designated CVE-2026-8037, affecting Progress Kemp LoadMaster application…
- Cybersecurity
- August 9, 2026
- 54 views
Elite Cyber Espionage Group Infiltrates TrueConf Infrastructure, Weaponizing Client Updates with Advanced Backdoors
A sophisticated and persistent cyber-attack campaign, attributed to a clandestine group known as Head Mare, has systematically exploited critical vulnerabilities within TrueConf’s widely adopted video conferencing platform, leading to the…
- Cybersecurity
- August 9, 2026
- 74 views
Sophisticated Supply Chain Attack Targets TrueConf, Injecting Backdoors into Client Installers
A highly sophisticated and targeted campaign, attributed to the group identified as Head Mare, has successfully compromised TrueConf video conferencing servers, systematically replacing legitimate client installers with trojanized versions that…
- Cybersecurity
- August 8, 2026
- 61 views
Insidious Digital Compromise: Nation-State-Linked Group Infiltrates TrueConf Infrastructure to Distribute Malicious Client Updates
A sophisticated cyber-espionage campaign has been uncovered, revealing how a threat actor, operating under the moniker Head Mare, has systematically breached TrueConf video conferencing servers to inject backdoors into client…

Presidential Edicts Signal Escalating Confrontation with the Fourth Estate
Aura Kasih
- September 19, 2026
- 9 views


Groundbreaking Discovery: New Guinea Serpent Unveiled and Named in Tribute to Rock Icon Slash
Ayu Aulia
- September 19, 2026
- 10 views

The Unsettling Enigma of Meta’s AI: A Deeper Dive into its Behavioral Quirks
- September 19, 2026
- 9 views


Scientists discover cells that cheat death and rebuild damaged tissue.
- September 19, 2026
- 7 views
