Safa Marwah
- Cybersecurity
- July 25, 2026
- 102 views
Global Operational Disruption Halts Access to OpenAI’s ChatGPT Platform
OpenAI’s immensely popular conversational artificial intelligence, ChatGPT, has experienced a substantial and widespread service disruption, rendering the platform inaccessible to a global user base and preventing access to both current…
- Cybersecurity
- July 24, 2026
- 106 views
OnTrac Reveals Network Compromise Exposing Customer Information
A significant cybersecurity incident has come to light involving OnTrac, a prominent parcel delivery enterprise, which recently confirmed a breach of its corporate network. The compromise potentially exposed sensitive personal…
- Cybersecurity
- July 24, 2026
- 89 views
Critical Vulnerability in PTC Windchill and FlexPLM Exploited by Clop Ransomware Group for Extensive Data Theft
A sophisticated data exfiltration campaign orchestrated by the notorious Clop ransomware syndicate is actively leveraging a critical security flaw within widely deployed Product Lifecycle Management (PLM) platforms, PTC Windchill and…
- Cybersecurity
- July 23, 2026
- 248 views
Emerging Dolphin X Malware Integrates Advanced AI for Sophisticated Victim Prioritization
A recently identified sophisticated remote access trojan, dubbed Dolphin X, is reportedly deploying an innovative artificial intelligence-driven profiling system designed to assess and prioritize compromised systems. This advanced capability aims…
- Cybersecurity
- July 23, 2026
- 92 views
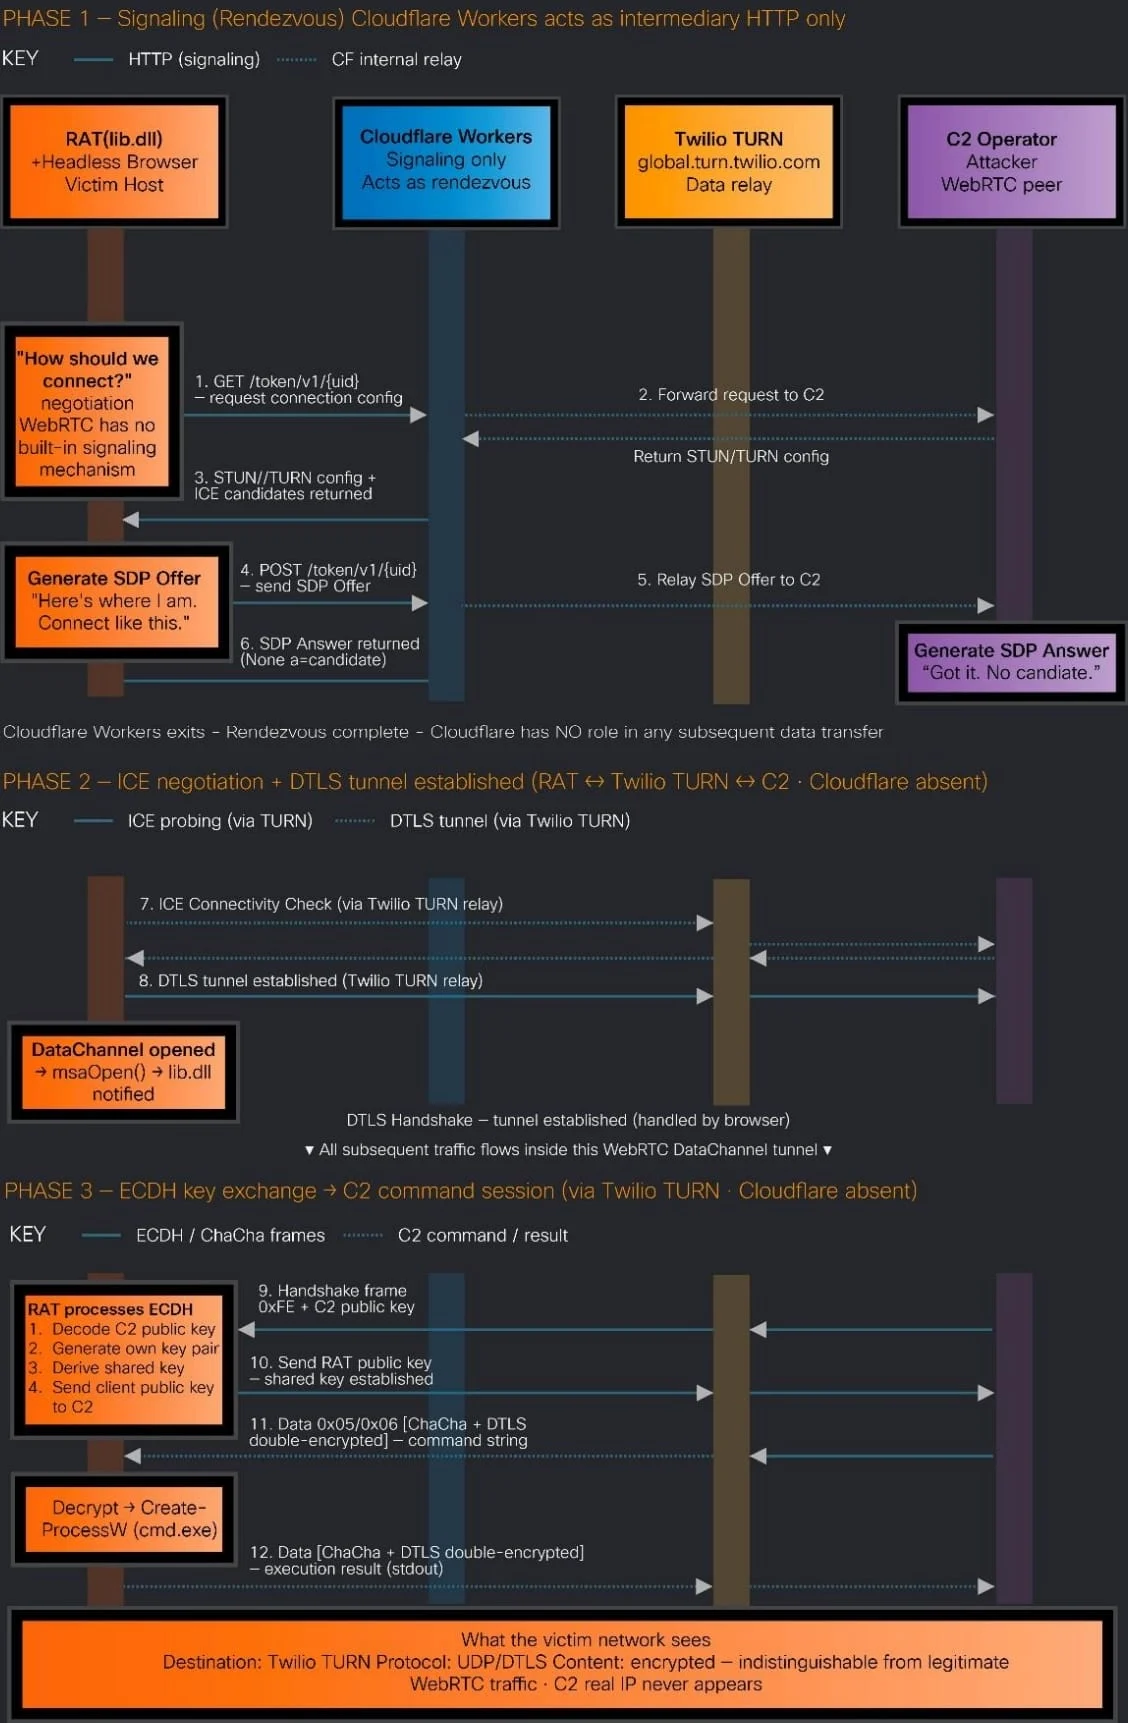
Sophisticated msaRAT Malware Exploits Browser Protocols for Covert Command and Control
A newly identified remote access Trojan (RAT), dubbed msaRAT, is being leveraged by the Chaos ransomware syndicate to establish highly evasive command-and-control (C2) channels by ingeniously routing communications through standard…
- Cybersecurity
- July 22, 2026
- 72 views
Cyberattack Leads to $13 Million Fraudulent Lease Scheme Against Upbound Group’s Acima Division
A sophisticated cyber incident impacting Upbound Group, a prominent player in alternative financial services, has resulted in an estimated $13 million in fraudulent lease-to-own agreements within its Acima segment during…
- Cybersecurity
- July 22, 2026
- 86 views
Digital Security Lapse Prompts Chick-fil-A to Alert Patrons Following Sophisticated Credential Exploits
A recent security incident has prompted Chick-fil-A, the prominent quick-service restaurant chain, to issue breach notifications to an undisclosed number of customers whose digital accounts were compromised during a series…
- Cybersecurity
- July 21, 2026
- 82 views
Critical SharePoint Remote Code Execution Flaw Exploited to Harvest Machine Keys and Subvert Content Security
Enterprise environments worldwide are confronting an escalating threat as a severe remote code execution (RCE) vulnerability within Microsoft SharePoint, identified as CVE-2026-50522, is being actively leveraged by malicious actors to…
- Cybersecurity
- July 21, 2026
- 89 views
Proactive Database Remediation Issued by Microsoft for Persistent WSUS Synchronization Failures
Enterprise IT departments are receiving critical manual intervention guidance from Microsoft to address a pervasive issue causing delays and outright timeouts in Windows Server Update Services (WSUS) synchronization processes, impacting…
- Cybersecurity
- July 20, 2026
- 134 views
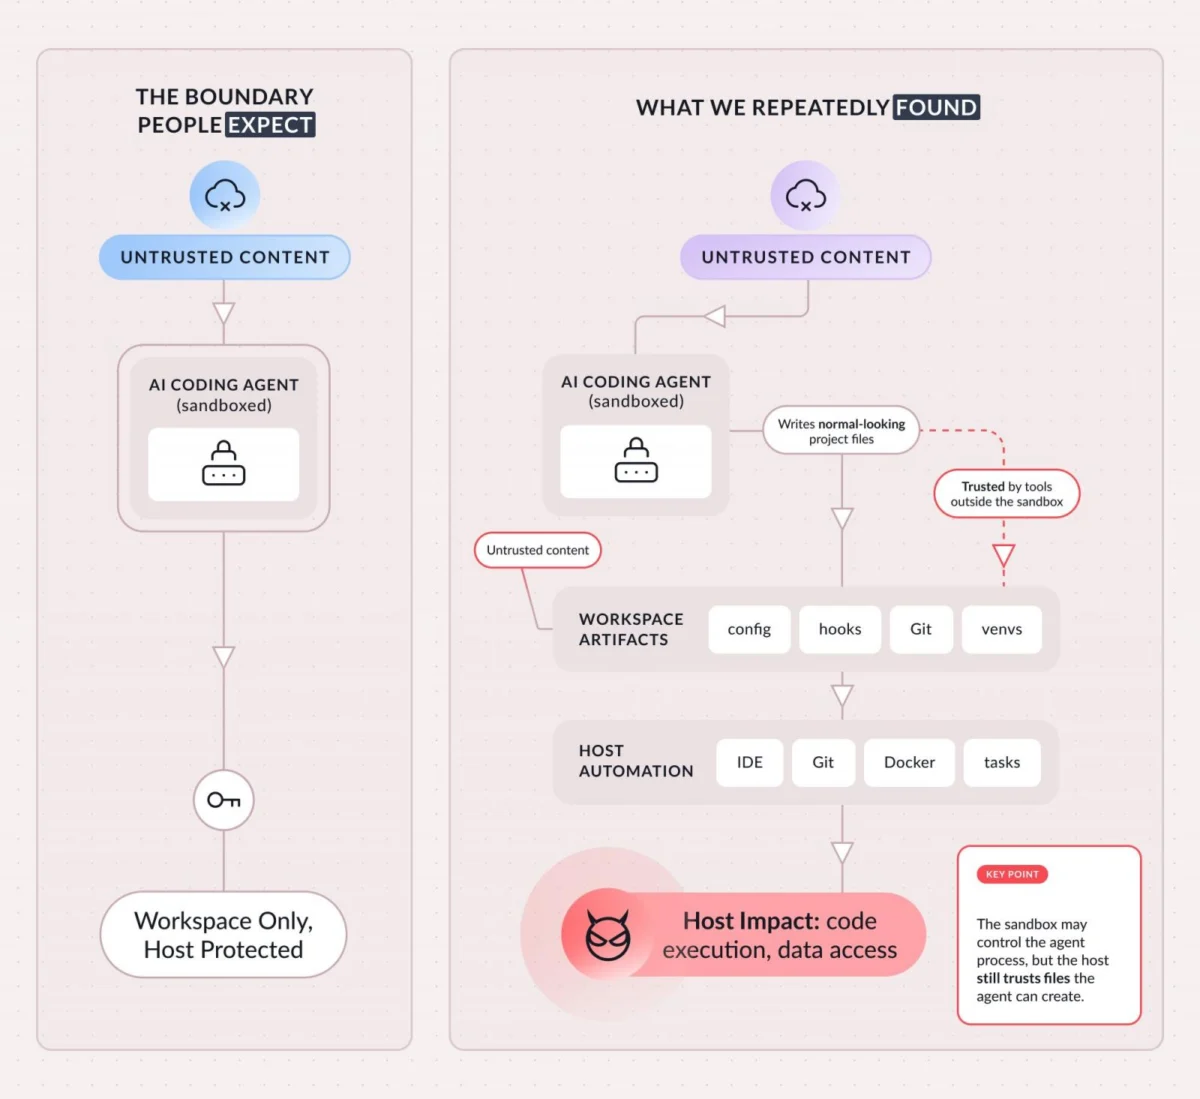
Unveiling a Sophisticated Threat: Autonomous AI Agents Breaching Sandboxes Through Indirect Command Execution
Recent investigations have revealed a novel class of security vulnerabilities impacting prominent AI-powered coding assistants, including Cursor, OpenAI’s Codex, Google’s Gemini CLI, and Antigravity, where agents circumvent their intended security…
Semiconductor Giant Pivots Towards Server Infrastructure as Mobile Market Stagnates
Aura Kasih
- November 4, 2026
- 1 views
 Ayu Aulia
 Lisa Mariana
Canva Undergoes Sweeping Restructuring, Impacting Over a Quarter of its Workforce
- November 3, 2026
- 1 views
